
ownCloud CVE-2023-49105 is a known-exploited vulnerability affecting self-hosted ownCloud Server 10 under specific conditions. ownCloud’s CVE-specific advisory lists core versions 10.6.0 through 10.13.0 as affected. CISA added the vulnerability to its Known Exploited Vulnerabilities catalog on August 27, 2026.
The key remediation distinction is that 10.13.3 is a historical CVE-era remediation reference, not the current latest ownCloud Server release. ownCloud’s security guidance says CVE-2023-49105 can be addressed by upgrading to 10.13.3 or applying the vendor patch where applicable, but ownCloud has since released newer supported Server versions, including 10.16.4 and ownCloud Classic 11.0.0. Administrators remediating a legacy deployment should use the current supported upgrade path and release documentation rather than deliberately stopping at 10.13.3.
Check whether your ownCloud Server is affected
You run ownCloud Server core 10.6.0 through 10.13.0
Your deployment falls within the CVE-specific affected range identified by ownCloud. Check the documented signing-key condition and remediate using current ownCloud guidance.
You run a later ownCloud Server release
Your version is outside the original CVE-specific affected range. Confirm the version actually deployed and make sure it is still on a currently supported and appropriately patched ownCloud Server branch.
You use Infinite Scale or managed ownCloud.Online
ownCloud says these products are not affected by this Server 10 vulnerability. Do not apply the ownCloud Server 10 version matrix to them.
Which ownCloud versions are affected by CVE-2023-49105?
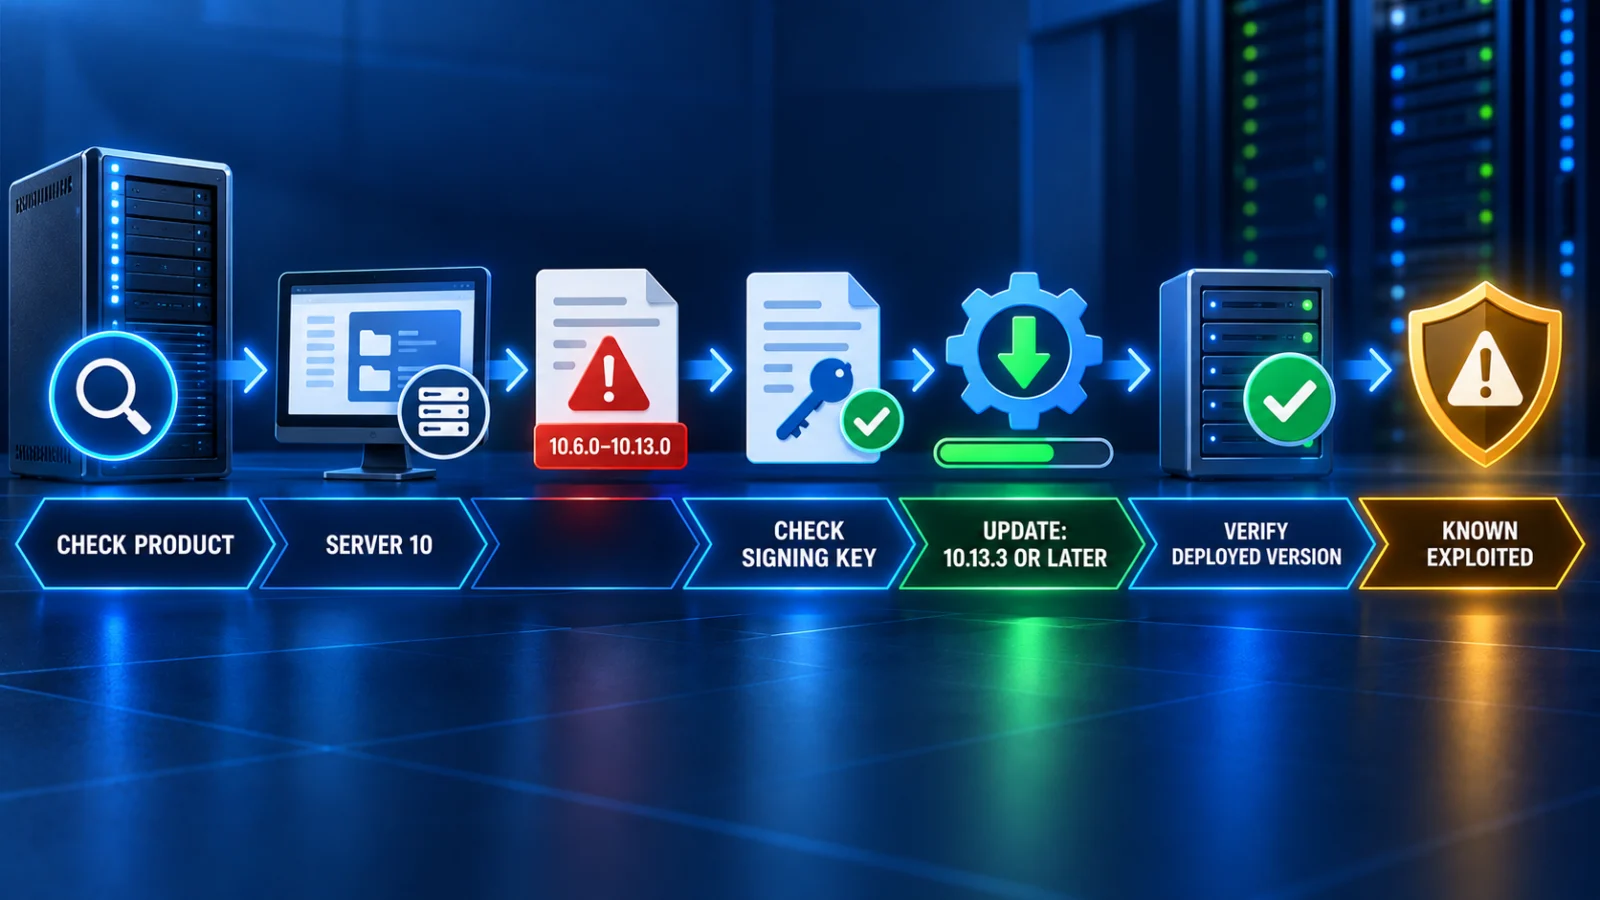
ownCloud’s direct advisory lists core 10.6.0 through 10.13.0 as affected by CVE-2023-49105.
The vulnerability concerns the WebDAV API and use of pre-signed URLs. According to ownCloud, exploitation requires the attacker to know the victim username and the victim user to have no signing key configured. ownCloud states that having no signing key configured is the default condition.
Why do 10.13.1, 10.13.3 and newer releases all matter?
They describe different points in the product’s security and release history.
- 10.13.0: the last affected core version listed in the direct CVE-2023-49105 advisory.
- 10.13.1: sits beyond the CVE-specific affected range and is part of the original fix-era history.
- 10.13.3: ownCloud’s broader security guidance explicitly recommends this version, or the vendor patch, for the WebDAV authentication-bypass issue.
- 10.16.4 and 11.0.0: ownCloud’s current release documentation now contains materially newer Server releases. Version 10.16.4 is described as a security release for which upgrading is strongly recommended, while 11.0.0 is a major release with additional security fixes and breaking changes.
For a current remediation decision, treat 10.13.3 as the historical minimum reference in ownCloud’s CVE-era guidance, not as a reason to remain on an old branch when a newer supported release is appropriate for your environment.
Can you upgrade directly to ownCloud 11?
ownCloud’s current upgrade documentation says supported 10.x installations can upgrade to 11.0.0, but administrators must review system requirements and release notes before doing so. ownCloud 11.0.0 raises the minimum PHP requirement to PHP 8.3 and includes breaking changes.
Before a major upgrade, ownCloud recommends a fresh backup, checking third-party application compatibility and reviewing the migration and release notes. An emergency CVE remediation decision should therefore separate two questions: whether the vulnerable state must be removed immediately, and which current supported release is operationally safe for that specific deployment.
What can CVE-2023-49105 allow?
Under the documented conditions, ownCloud says an unauthenticated attacker can access, modify or delete files through the affected WebDAV path. That creates confidentiality and integrity risk for data held on a vulnerable self-hosted Server deployment.
What should ownCloud Server administrators do?
- Confirm which ownCloud product you operate: Server, Infinite Scale or managed ownCloud.Online.
- If you run ownCloud Server, confirm the exact core version actually deployed.
- If the server falls within the CVE-specific affected range, review whether the documented signing-key condition applies.
- Remove the vulnerable state using ownCloud’s supported remediation route. The CVE-era guidance identifies 10.13.3 or the vendor patch where applicable.
- For a lasting operational target, check the current ownCloud Server release notes and upgrade documentation rather than assuming 10.13.3 is still the newest appropriate destination.
- Before moving to a newer major release such as 11.0.0, verify PHP requirements, third-party-app compatibility, backup readiness and documented migration requirements.
- After remediation or upgrade, verify the version actually deployed and confirm that the service returned to the expected operational state.
Is CVE-2023-49105 actively exploited?
Yes. CVE-2023-49105 remains listed in CISA’s Known Exploited Vulnerabilities catalog. Its August 27, 2026 addition establishes observed exploitation in the wild.
This exploitation state increases remediation urgency, but it does not prove that every vulnerable ownCloud Server was attacked or compromised.
Does the CISA remediation requirement apply to every organization?
No. CISA KEV is strong evidence that exploitation has occurred, but U.S. federal remediation requirements apply within the relevant federal directive framework. Private organizations and operators in other jurisdictions should not treat a CISA federal deadline as their own legal deadline unless another applicable authority or policy makes it so.
What does patching establish?
Updating or patching and then verifying the deployed ownCloud Server state establishes that the known vulnerable software condition has been addressed according to the applicable remediation path.
It does not establish whether unauthorized file access, modification or deletion occurred before remediation. That historical question requires evidence from the individual environment and cannot be answered from the installed version alone.
Are there ownCloud-specific indicators of compromise?
TPS did not recover a complete authoritative CVE-2023-49105-specific indicator-of-compromise or forensic checklist from the reviewed primary sources.
For that reason, this article does not invent file names, log signatures or attacker artifacts. Administrators with evidence of suspicious access or other anomalies should follow their established incident-response and forensic process while preserving relevant logs and system evidence.
Limitations & unresolved facts
- The number of organizations currently running a vulnerable ownCloud Server version is unknown.
- The scale and geographic breadth of exploitation are not established by the reviewed primary evidence.
- TPS cannot determine whether a particular ownCloud deployment was compromised.
- No complete authoritative CVE-specific forensic or indicator-of-compromise checklist was recovered.
- The correct current upgrade destination can depend on the deployment’s PHP version, third-party apps and other system requirements.
Verification method
ThePulseSignal reviewed ownCloud’s direct CVE-2023-49105 advisory, current security guidance, current Server changelog and release notes, ownCloud’s upgrade documentation and the CISA known-exploitation state. The evidence separates the original CVE-specific affected range and 10.13.3 remediation reference from the materially newer ownCloud Server releases now available.
Frequently asked questions
Which ownCloud versions are affected by CVE-2023-49105?
ownCloud’s direct CVE advisory lists core versions 10.6.0 through 10.13.0.
Should I upgrade to ownCloud 10.13.1 or 10.13.3?
Do not choose a legacy release solely because it appears in the original CVE history. ownCloud’s CVE-era security guidance names 10.13.3 or a vendor patch, while current release documentation contains newer supported releases. Use the current supported upgrade path that is compatible with your deployment.
Is ownCloud 10.13.3 still the latest Server release?
No. ownCloud’s current release documentation includes newer releases such as 10.16.4 and ownCloud Classic 11.0.0.
Is ownCloud Infinite Scale affected?
ownCloud says Infinite Scale is not affected by this Server 10 issue.
Is managed ownCloud.Online affected?
ownCloud says managed ownCloud.Online is not affected by this Server 10 issue.
Is CVE-2023-49105 actively exploited?
Yes. CISA added CVE-2023-49105 to the Known Exploited Vulnerabilities catalog on August 27, 2026.