






The IBM Guardium 12.2 security update addresses multiple serious vulnerabilities in Guardium Data Protection 12.2. IBM’s September 17 security bulletin directs affected 12.2 deployments to the 12.0p233 fix pack and lists no workaround.
The most important point for administrators is that the vulnerabilities do not all have the same attack prerequisites. Some can be reached without authentication under the conditions described by IBM, while others require an authenticated or otherwise more limited position. TPS therefore does not treat the entire bulletin as one generic unauthenticated-RCE issue.
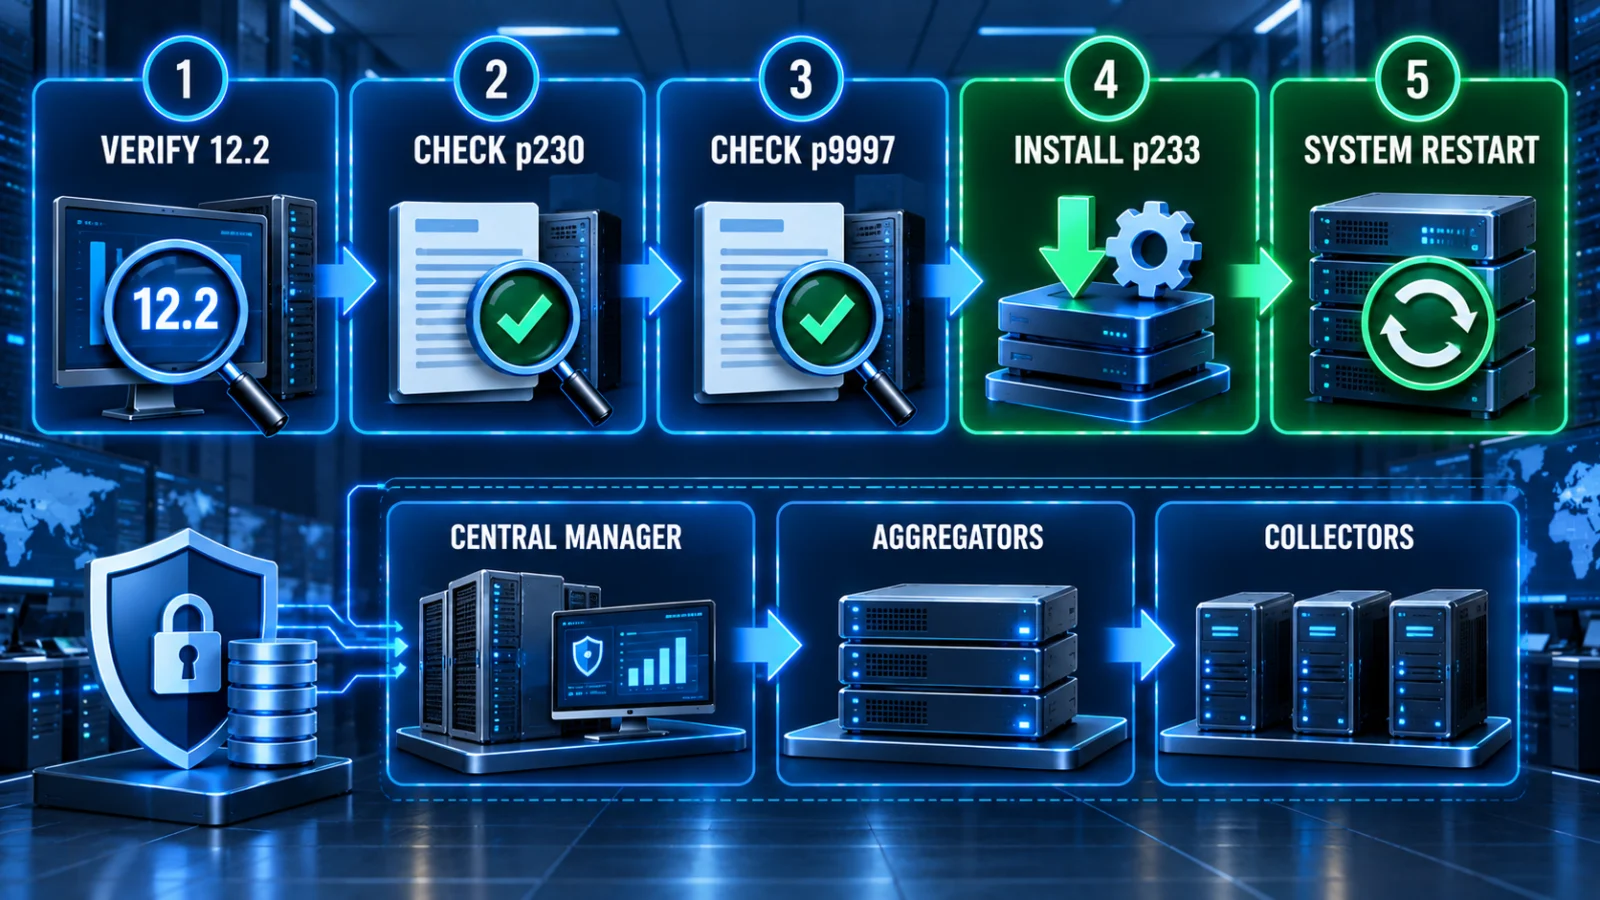
Confirm that the appliance is running Guardium Data Protection 12.2 and record its current patch level before planning remediation.
IBM’s p233 release notes require the p230 patch level and the current p9997 health-check patch before installation.
IBM says installation of p233 restarts the Guardium system, so administrators should treat the change as production maintenance rather than a background package update.
For distributed environments, IBM instructs administrators to install from the top down: central manager first, then aggregators, then collectors.
IBM’s p234 documentation lists p233 as a prerequisite, so the existence of a later patch should not be interpreted as permission to skip the documented p233 dependency.
Verify the latest IBM bulletin and fix-pack notes immediately before deployment in case affected scope, prerequisites or remediation guidance changes.
Which Guardium version is affected?
IBM’s bulletin identifies Guardium Data Protection 12.2 as the affected product level for this security update. Administrators should not automatically extend that exact bulletin scope to Guardium 12.0, Guardium 12.1, Guardium Insights or unrelated Guardium components unless IBM separately identifies them.
Why is the IBM Guardium 12.2 security update important?
The bulletin groups several vulnerability classes that can affect the confidentiality or control of a Guardium deployment. The reviewed evidence includes critical issues involving unsafe deserialization, missing authentication, SQL injection and command execution.
Examples include CVE-2026-81657, CVE-2026-82340, CVE-2026-84078, CVE-2026-80441, CVE-2026-80442 and CVE-2026-84082. Their access requirements differ, which is why administrators should review the CVE-specific conditions rather than assuming every vulnerability is remotely exploitable in the same way.
Which fix does IBM prescribe?
For the reviewed Guardium Data Protection 12.2 bulletin, IBM directs affected deployments to SqlGuard_12.0p233_FixPack. IBM also states that no workaround is available for the bulletin.
That means exposure reduction measures should not be presented as a substitute for IBM’s documented remediation. Network controls may still be part of normal defence-in-depth, but TPS did not find an IBM-documented workaround that replaces the fix pack.
What must be installed before p233?
IBM’s p233 release notes state that the Guardium system should already be on the p230 patch level and have the current p9997 health-check patch. Administrators should verify both prerequisites rather than treating p233 as a standalone package that can be installed on any 12.2 patch level.
The same release notes say installing p233 restarts the Guardium system. That creates a maintenance-window and availability consideration for production environments.
What is the correct patch order for multiple Guardium appliances?
IBM recommends a top-down installation order for managed deployments: central manager first, then aggregators, then collectors. That order should be preserved when planning a multi-appliance change rather than patching systems arbitrarily.
Organizations should still apply their own change-control, backup and availability procedures around the IBM sequence, because the reviewed IBM documentation establishes the product patch order but does not describe each customer’s environment-specific resilience plan.
Can administrators skip directly to p234?
TPS does not recommend describing p234 as a replacement for the p233 requirement. IBM’s reviewed p234 release documentation lists p233 as a prerequisite. The existence of a numerically later patch therefore does not, by itself, prove that an administrator can bypass the required p233 step.
Are these Guardium vulnerabilities actively exploited?
TPS did not establish active exploitation from the reviewed IBM material or other authoritative evidence available during this research. The vulnerabilities are serious because of their documented technical impact and high severity, but severity is not the same as confirmed exploitation in the wild.
Administrators should therefore avoid two opposite mistakes: delaying remediation because exploitation has not been confirmed, or describing the update internally as an active-exploitation incident without evidence.
What should Guardium administrators verify before patching?
- The appliance is Guardium Data Protection 12.2 and is covered by the IBM bulletin.
- The current installed patch level is recorded.
- The p230 prerequisite is satisfied.
- The current p9997 health-check patch requirement is satisfied.
- A maintenance window accounts for the documented restart.
- Central managers, aggregators and collectors are scheduled in IBM’s stated order.
- The latest IBM bulletin and release notes have been rechecked for revisions immediately before deployment.
What remains uncertain?
The reviewed evidence does not establish exploitation in the wild, undisclosed customer incidents or whether IBM will revise the affected-version scope. Environment-specific exposure also depends on which Guardium services are reachable and which authentication or network conditions apply to each CVE.
TPS also does not treat every vulnerability in the bulletin as an unauthenticated remote-code-execution path. Authentication and component prerequisites must remain attached to the individual CVE descriptions.
What could change next?
This article should be updated on the same URL if IBM revises bulletin 7288040, changes the affected or fixed-version scope, publishes a new workaround or mitigation, changes the fix-pack path, or if CISA or another authoritative body confirms active exploitation or adds a covered CVE to a high-priority exploitation catalog.
Verification note
ThePulseSignal reviewed IBM’s Guardium Data Protection security bulletin together with IBM’s p233 and p234 patch documentation to reconcile the affected product, remediation package, prerequisites, restart requirement and deployment order. Active exploitation was not established in the reviewed evidence.