






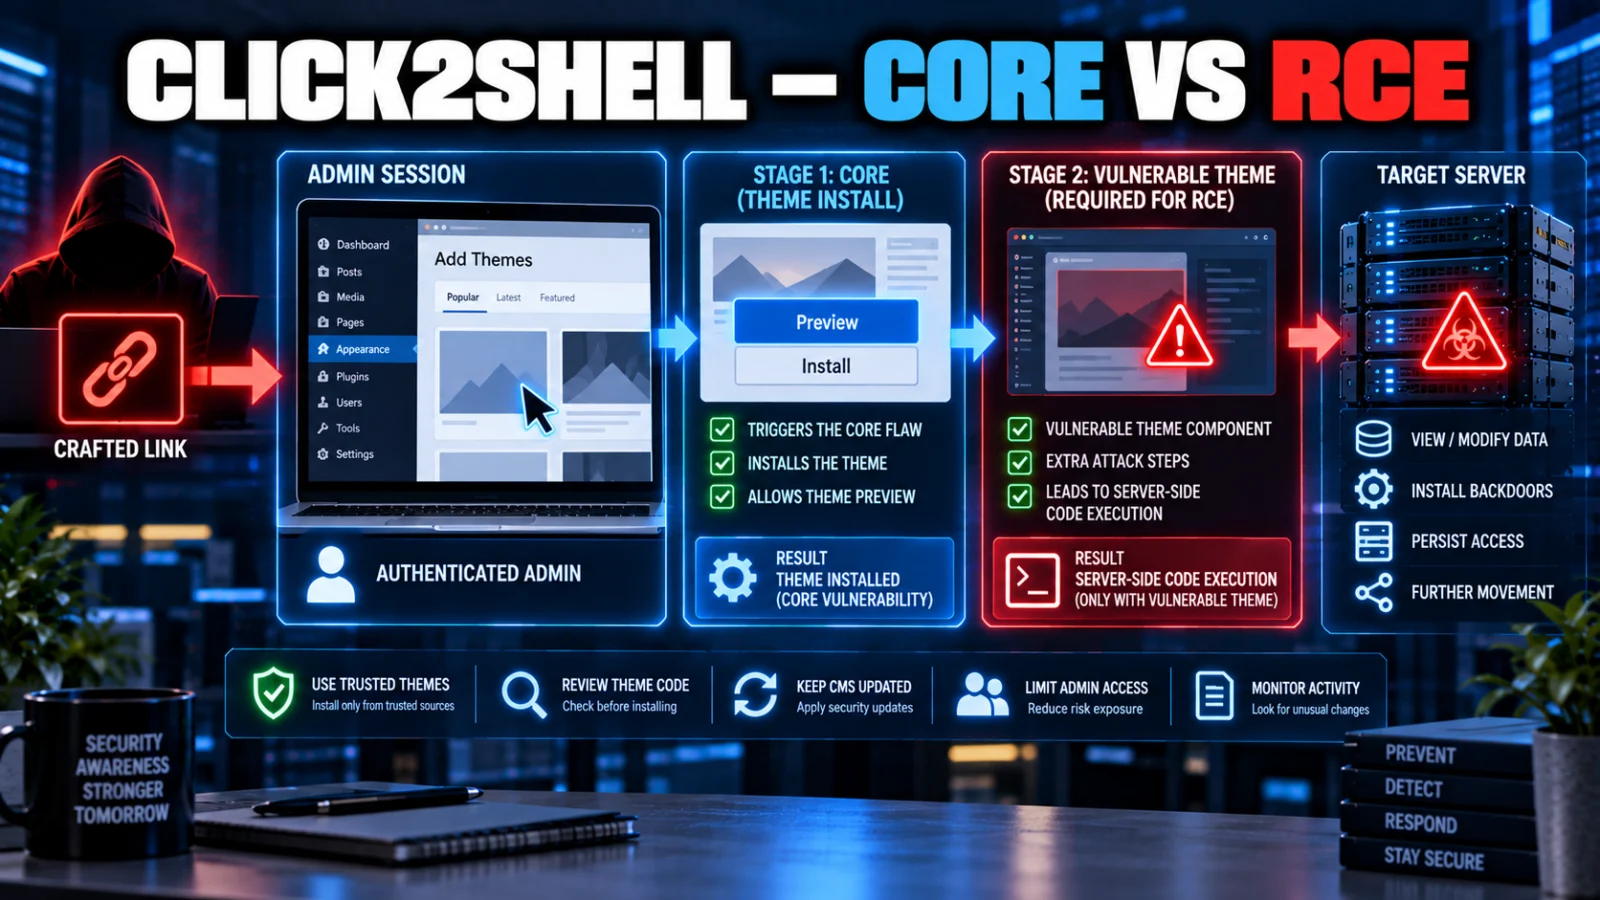
The Click2Shell WordPress flaw patched in WordPress 7.1.1 can let a crafted link opened by a logged-in administrator trigger installation and preview of an attacker-selected theme from the official WordPress.org catalog. The important boundary is that the WordPress Core issue by itself is not the same as arbitrary remote code execution. Researchers demonstrated full PHP execution only by chaining the forced theme-install primitive with a separate vulnerability in a theme.
What administrators should do: verify the site’s WordPress version and install WordPress 7.1.1 or the corresponding September 17 patched maintenance release for the branch in use. If there is reason to suspect exposure, inspect for unexpected theme installations or other unauthorized changes. Do not treat an inactive theme by itself as proof of compromise.
What exactly did WordPress patch?
WordPress describes the issue as a crafted URL that could cause the theme installer and preview flow to install and preview a theme from WordPress.org. The problem was corrected in the September 17 security releases, including WordPress 7.1.1 for the current branch.
The flaw is security-relevant because the attacker’s request can make use of an already authenticated administrator session. The attacker does not need their own WordPress account, but the demonstrated path depends on a privileged user being logged in and opening the crafted link or page.
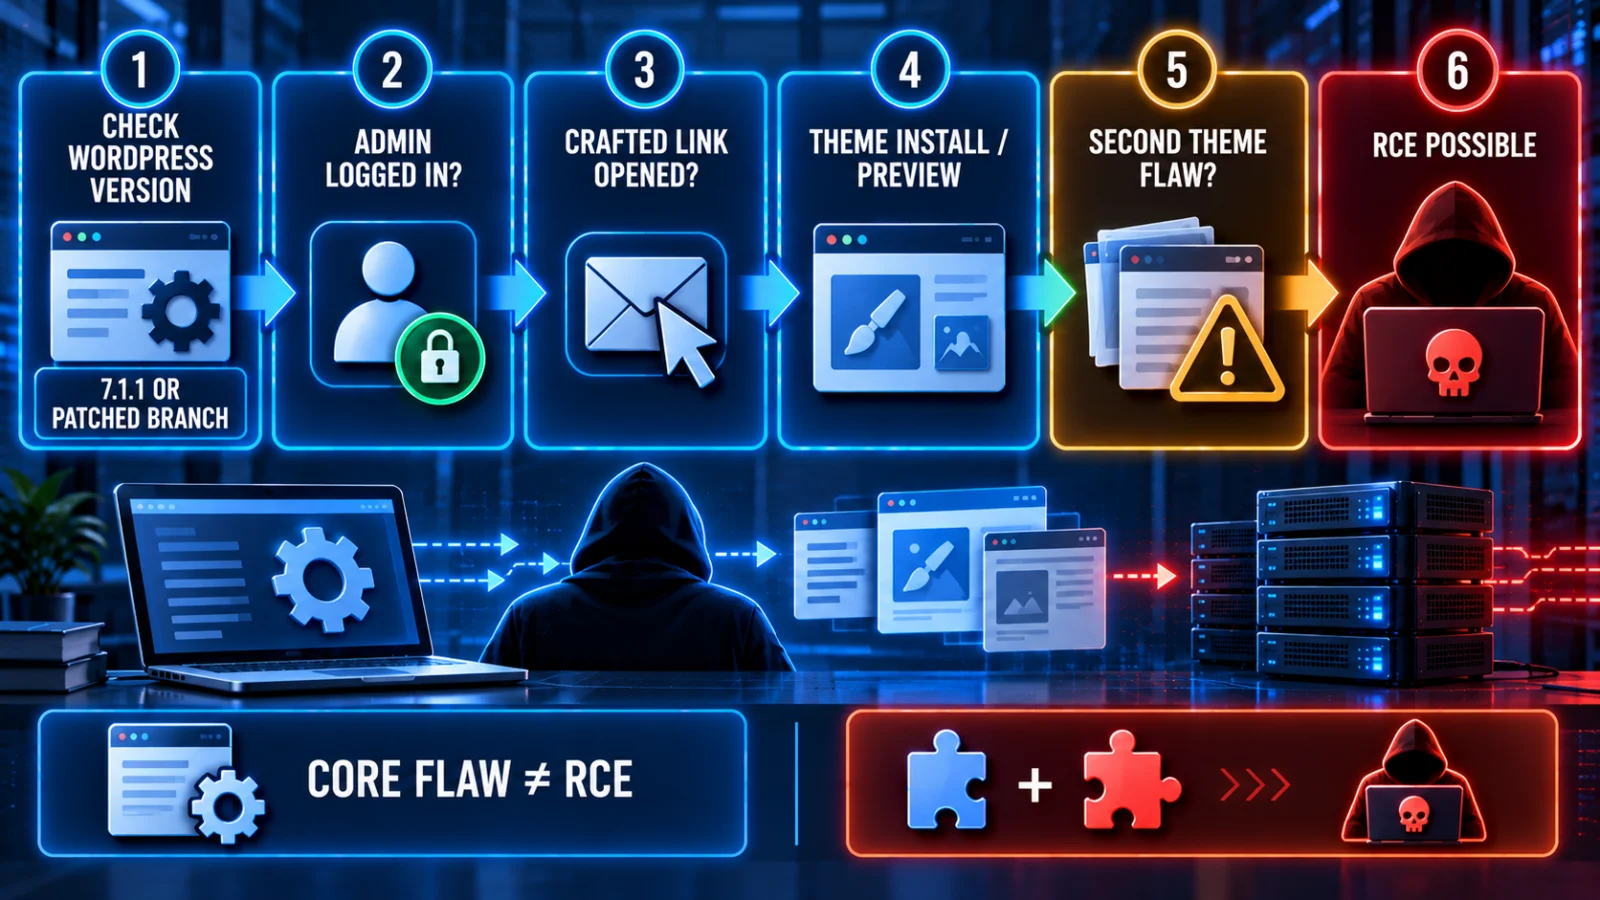
Does Click2Shell mean WordPress Core has instant unauthenticated RCE?
No. The Core flaw lets an attacker influence which WordPress.org theme is installed and previewed through the administrator’s authenticated browser session. The full code-execution demonstration required a second weakness in theme code.
That distinction matters. A headline that describes the Core issue alone as universal one-click remote code execution would overstate what the reviewed evidence proves.
How the demonstrated RCE chain works
Researchers at pwn.ai demonstrated the chain using Mobile Repair Zone 2.5.4. After the Core issue forced installation and preview of the theme, a separate pre-activation theme weakness could be reached and used to execute PHP code.
The research therefore establishes a chain: Core theme-install behavior creates the opening, while a vulnerable theme or other compatible code path supplies the additional condition needed for PHP execution.
How to decide what your site needs
If the site is on the current branch, verify that WordPress 7.1.1 or a later security release is installed. Older supported branches received their own September 17 security maintenance releases.
Sites intentionally maintained on older supported branches should verify the corresponding security release rather than using version 7.1.1 as the only possible fixed state.
The demonstrated Click2Shell path depends on a logged-in administrator opening attacker-controlled content. An attacker having no WordPress account does not mean the exploit requires zero victim interaction.
The Core primitive can force a theme install and preview. Full PHP execution additionally requires an exploitable theme or compatible second-stage weakness.
If a privileged user may have opened a suspicious link before the update, inspect for unexpected newly installed themes or other unauthorized site changes and escalate to incident response if evidence of compromise is found.
Which WordPress versions are fixed?
WordPress 7.1.1 contains the fix for the current branch. WordPress also issued corresponding September 17 security maintenance releases for older supported branches, so administrators should verify the correct patched release for the version family they intentionally maintain.
The oldest branch deserves extra caution. WordPress’s broader release guidance says eligible security backports extend through older branches, while an independent branch-by-branch review reported that the specific Click2Shell entry was not visible in WordPress 4.7.36. Until WordPress clarifies that edge case, TPS should not state unconditionally that 4.7.36 either definitely contains or definitely lacks this exact fix.
Does every WordPress theme make Click2Shell an RCE?
No. The demonstrated RCE used a separate weakness in Mobile Repair Zone 2.5.4. pwn.ai also reported finding similar unsafe pre-activation patterns in more than 40 other themes, but the reviewed evidence did not provide a complete validated list of all affected themes.
Administrators should therefore avoid assuming that every theme is vulnerable while also avoiding the opposite assumption that an inactive theme is harmless in every pre-activation code path.
Is there a CVE for Click2Shell?
No CVE was listed in the reviewed original disclosure. pwn.ai said WordPress was working on assignment. That status can change, so a later CVE or formal security advisory should update this same article rather than create a new URL.
Is Click2Shell being exploited in the wild?
No confirmed active exploitation was found in the current sources reviewed for this article. That is a current evidence state, not a guarantee that exploitation has not occurred or will not emerge later.
What should administrators check after updating?
First confirm that the security update actually completed. If there is a plausible exposure path, review the site’s theme list and relevant administrative activity for unexpected changes around the suspected period. A newly installed theme can be an investigation clue, but its presence alone does not prove Click2Shell exploitation.
If evidence shows unauthorized code execution, unexpected administrator actions, file changes or persistent access, move from patch verification into a full incident-response process rather than assuming the Core update alone removes all effects of a successful compromise.
Verification and limitations
The Core security state and update recommendation were checked against WordPress’s September 17 security release and version documentation. The forced theme-install and chained RCE behavior were checked against pwn.ai’s original Click2Shell research, with current independent security reporting used to review exploitation status and branch-specific uncertainty. CVE assignment, WordPress’s final severity assessment, confirmed in-the-wild exploitation, the complete affected-theme list and the exact 4.7.36 backport state remain unresolved.
Bottom line: update WordPress to the appropriate September 17 patched release, but interpret the security issue precisely. Click2Shell’s Core flaw can force installation and preview of an official catalog theme through a logged-in administrator session; the demonstrated RCE requires an additional vulnerable theme or code path.