






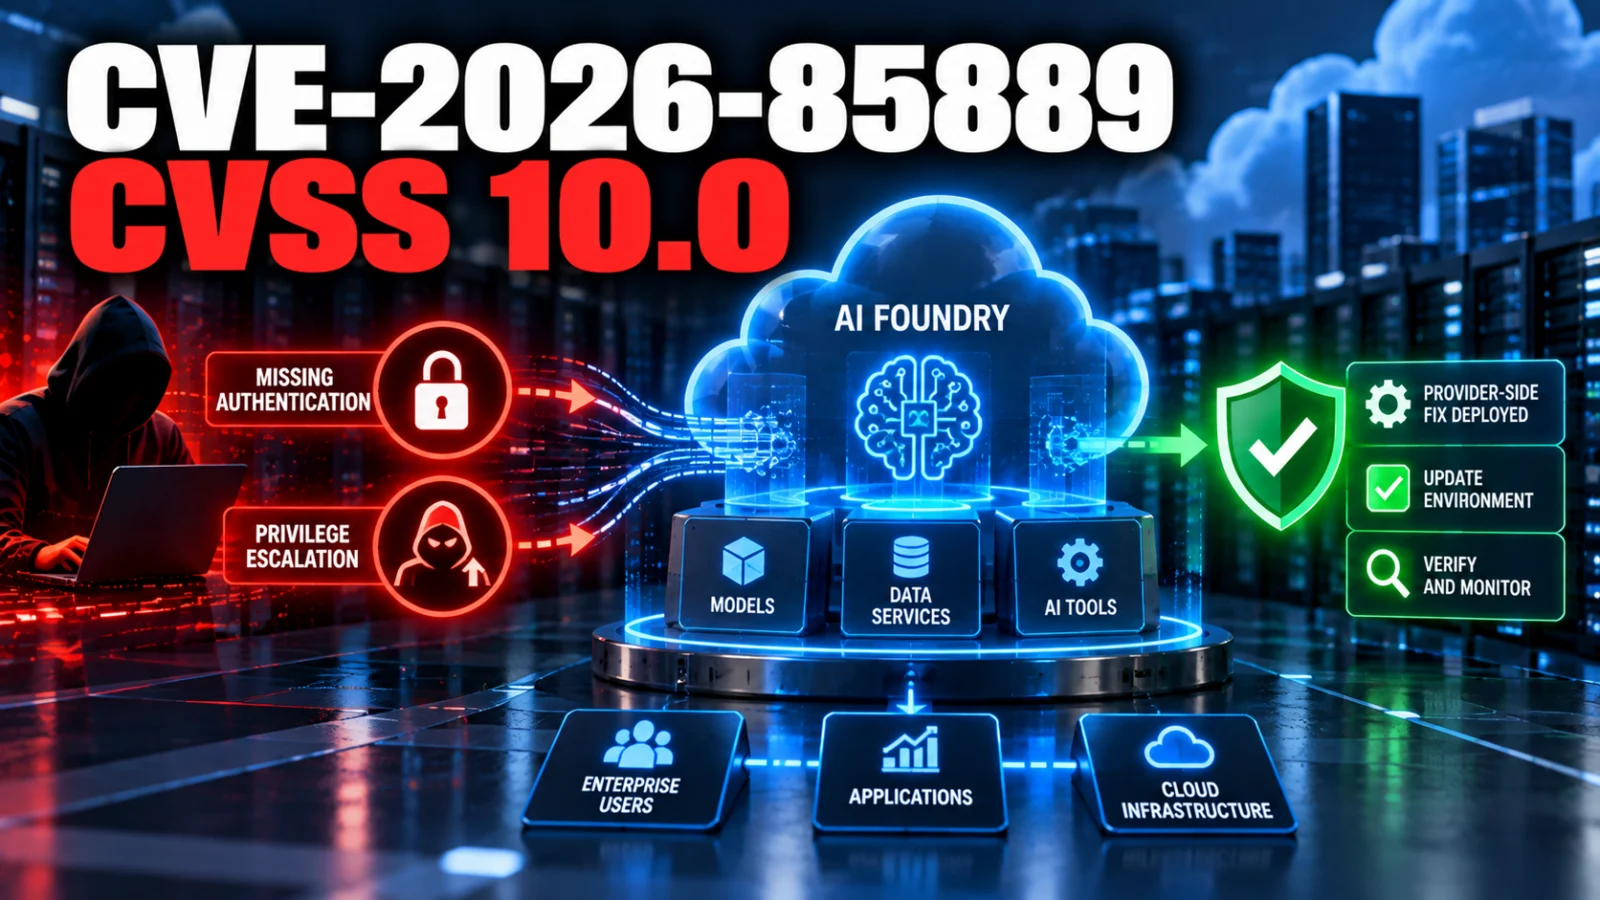
CVE-2026-85889 is a maximum-severity vulnerability affecting Microsoft Azure AI Foundry. Microsoft-assigned CVE data gives the flaw a CVSS 3.1 score of 10.0 and classifies it as CWE-306: Missing Authentication for Critical Function. The vulnerability can be reached over the network with low attack complexity, requires no prior privileges and requires no user interaction.
The most important point for Azure AI Foundry customers is that severity and remediation ownership are not the same thing. Current reporting citing Microsoft’s advisory says Microsoft has already mitigated the vulnerable hosted-service component and that no customer action is required. That means customers should not interpret the CVSS 10.0 score as an instruction to search for or install a tenant-side patch that Microsoft has not asked them to deploy.
What CVE-2026-85889 allows
Microsoft’s CVE description says an unauthorized attacker could exploit missing authentication to elevate privileges over a network. The assigned CVSS vector is consistent with a remotely reachable, low-complexity flaw that does not require an authenticated account or user interaction and can have high confidentiality, integrity and availability impact.
The reviewed evidence does not establish the precise Azure AI Foundry backend function that was missing authentication. TPS is therefore not attributing the flaw to a particular model endpoint, dataset, API, credential store or tenant resource unless Microsoft later provides that level of technical detail.
Do Azure AI Foundry customers need to patch?
Based on current Microsoft-attributed reporting, no customer-installed patch is required. Microsoft reportedly remediated the issue within the managed Azure service itself. This distinction matters because generic vulnerability databases sometimes use boilerplate such as “apply the vendor patch” even when the affected component is operated entirely by the cloud provider.
For this CVE, the safer reader action is to verify the current Microsoft Security Response Center status, record the vulnerability in internal security or risk tracking where relevant, and monitor for any change in Microsoft’s customer-action guidance. Administrators should not substitute an unrelated Azure update or make production changes solely because the CVSS score is 10.0.
Was CVE-2026-85889 exploited?
Current reporting citing Microsoft says there was no evidence of exploitation in the wild at disclosure time. That statement should not be read as proof that exploitation could never have occurred. TPS has not identified Microsoft-published tenant-level detection guidance, forensic indicators or a supported procedure that customers can use to independently prove historical non-exploitation for this CVE.
Why a CVSS 10.0 flaw can still require no customer patch
CVSS measures the technical severity and exploitability of a vulnerability; it does not determine who owns the remediation. In a fully managed cloud service, the vulnerable code can reside in infrastructure controlled by the provider. If Microsoft fixes that provider-side component before or at disclosure, the vulnerability can remain technically critical while the customer’s required remediation is simply to confirm the vendor’s current status and monitor for further guidance.
This is the practical distinction TPS found most useful in the current result set: CVE-2026-85889 is serious, but the current response is not “patch Azure AI Foundry yourself.” The response is to understand Microsoft’s service-side mitigation state and watch for any later advisory revision that changes the customer’s responsibilities.
What remains unresolved
The reviewed evidence does not establish the exact vulnerable backend component, the precise historical exposure window, tenant-visible indicators of compromise or a Microsoft-supported forensic workflow for this CVE. TPS also did not independently render the complete MSRC FAQ body during research, so the service-side mitigation, no-customer-action and no-known-exploitation statements are retained as Microsoft-attributed current reporting rather than upgraded beyond the available evidence.
What could change next
This article should be updated on the same URL if Microsoft revises CVE-2026-85889, publishes deeper root-cause or detection guidance, changes its customer-action position, or if Microsoft, CISA or another authoritative security source reports exploitation. Until then, the current evidence supports a clear operational distinction: the vulnerability is confirmed and maximum severity, while Microsoft reportedly owns the remediation for the hosted service.