






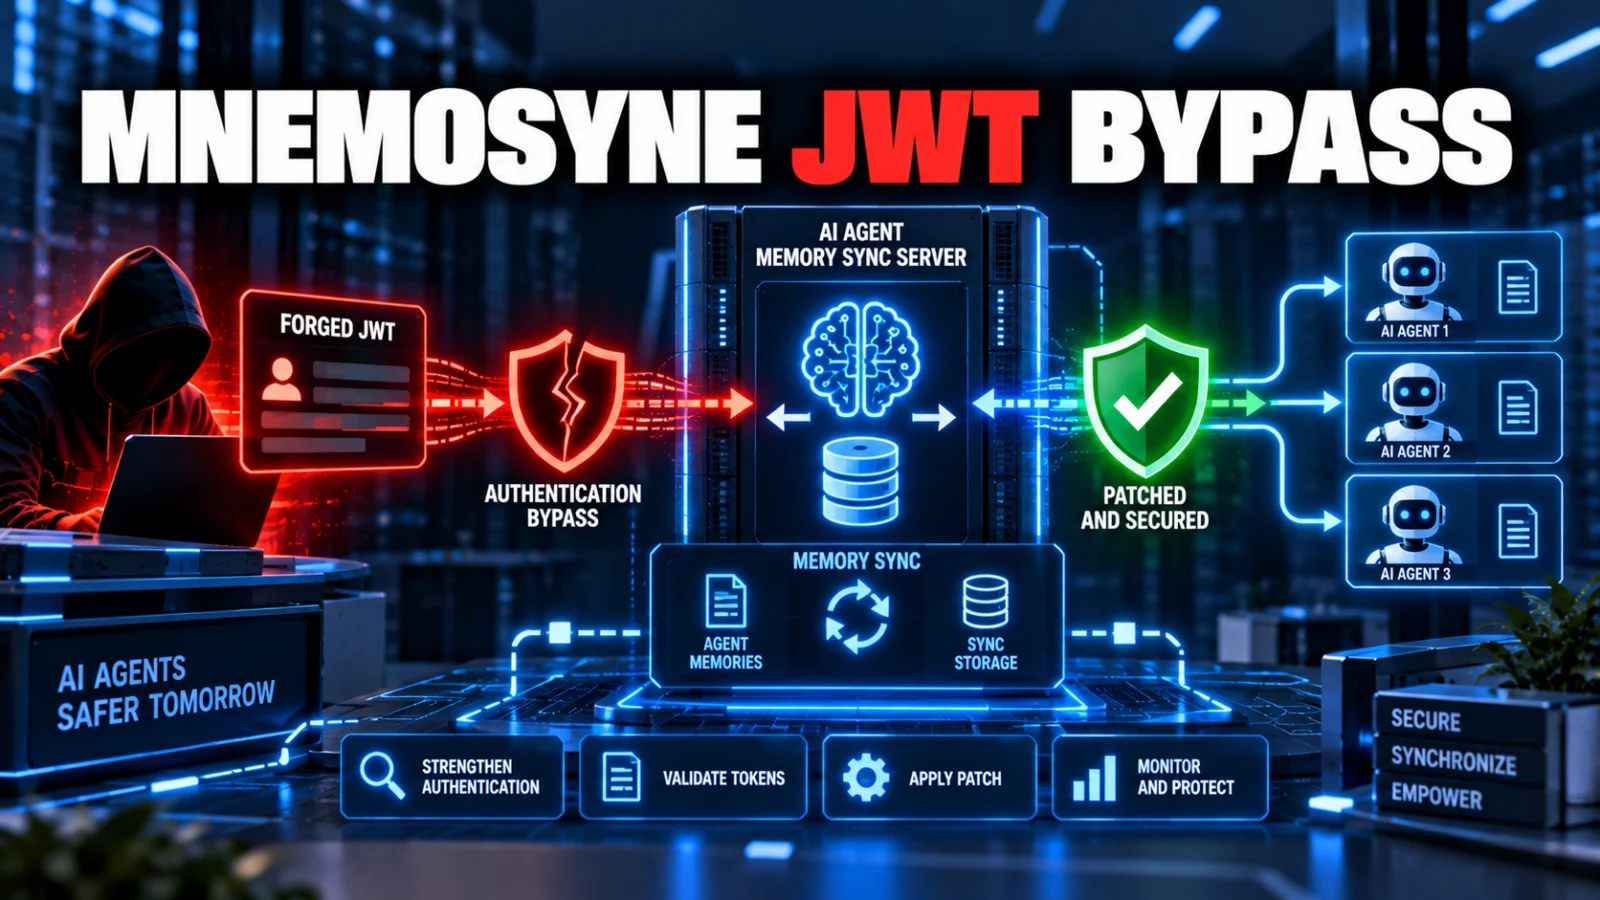
CVE-2026-59163 is a critical authentication vulnerability in the Mnemosyne sync server. The reviewed security advisories say affected versions can decode a JSON Web Token without properly verifying its cryptographic signature. If an attacker can reach a vulnerable sync endpoint, a forged token may be accepted as authenticated, allowing user impersonation and unauthorized access to synchronized memory data.
Direct answer: Mnemosyne deployments running version 3.10.0 or earlier should be treated as affected. Version 3.10.1 contains the security fix. Practical remote exposure depends on whether an untrusted attacker can reach the vulnerable sync endpoint.
CVE-2026-59163 affected versions and fix
The reviewed GitHub security advisory, OSV record and Mnemosyne project release information agree on the important version boundary: releases before 3.10.1 are affected, while 3.10.1 fixes the JWT signature-verification problem. Operators should first identify the exact Mnemosyne version running on the sync server rather than assuming every installation has the same exposure.
Why network reachability matters
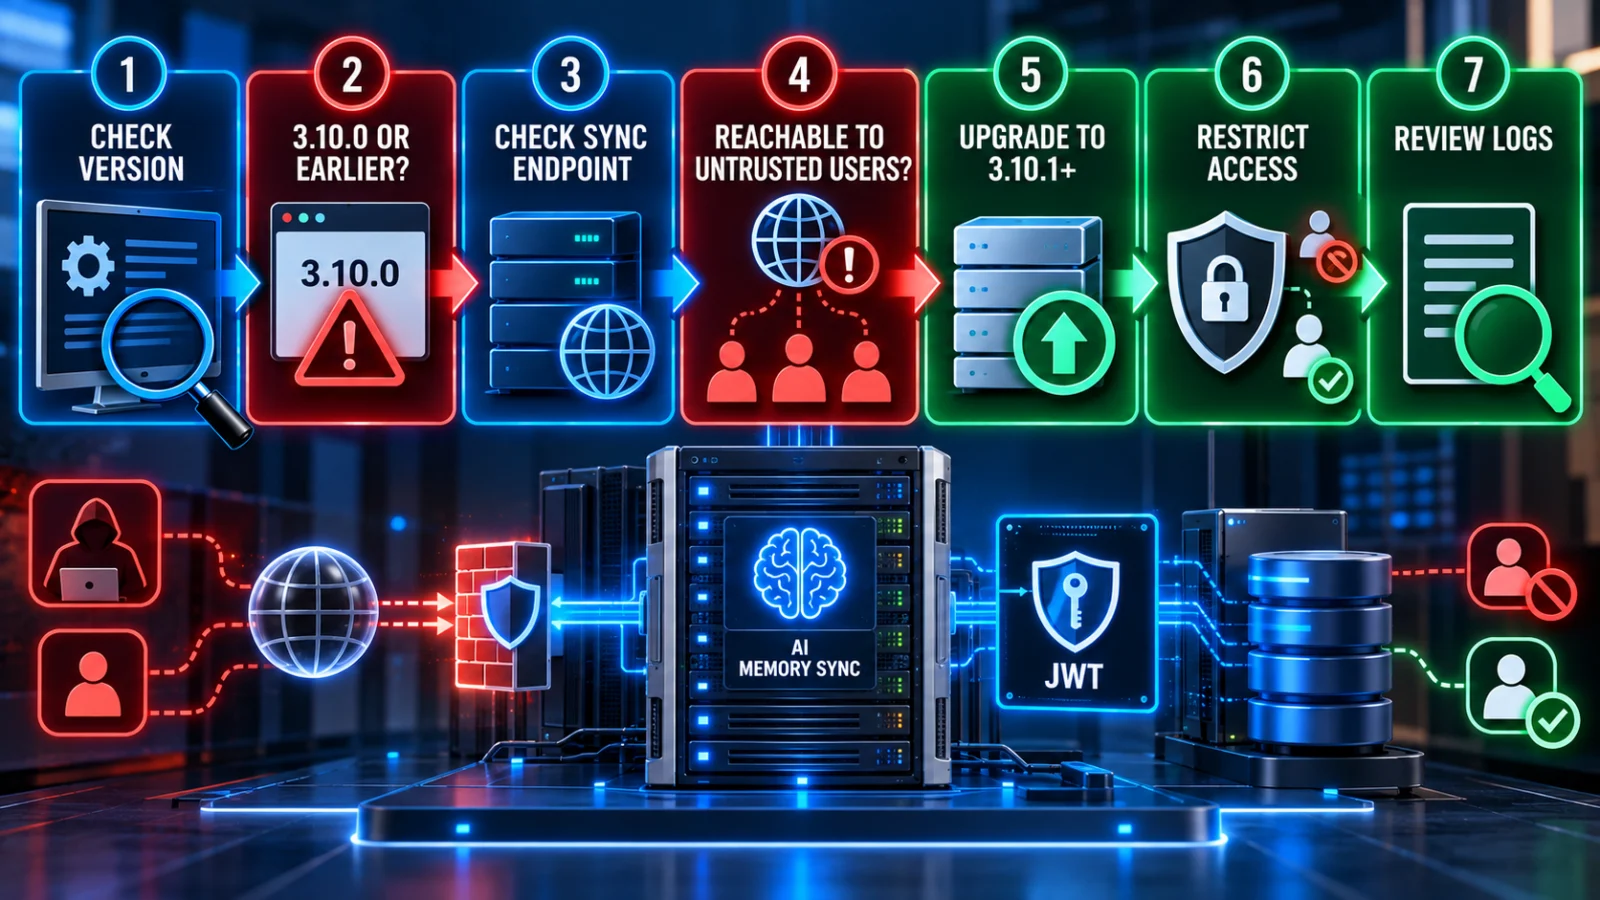
This vulnerability is not equivalent to saying every Mnemosyne installation is already compromised. The attack requires an adversary to interact with a vulnerable sync endpoint. A server reachable from untrusted networks therefore presents a materially different risk from a deployment whose sync endpoint is tightly restricted. Version state and reachability should be evaluated together.
If the sync server is on 3.10.0 or earlier, continue as an affected deployment.
Determine whether untrusted users or external networks can reach the vulnerable sync service.
Move to Mnemosyne 3.10.1 or a later fixed release supported by the project.
Restrict access to the sync endpoint while the vulnerable version remains deployed.
If logs or other telemetry show suspicious authentication or data-access activity, investigate that separately rather than assuming the upgrade alone proves the environment was never abused.
What an attacker could do
Because the flaw affects authentication, successful exploitation can let an attacker impersonate another user. The reviewed advisory material says this can expose synchronized memory information and permit unauthorized modification of that data. For AI-agent systems that rely on synchronized memory as persistent context, unauthorized changes could also affect what an agent later retrieves from that store.
What the disclosure does not establish
ThePulseSignal did not find controlling evidence in the reviewed sources showing that CVE-2026-59163 is being actively exploited in the wild. The reviewed material also does not establish that every vulnerable deployment was internet-accessible or compromised. TPS therefore does not describe this as an active breach.
The reviewed evidence also does not establish a project-wide requirement to rotate JWT secrets, invalidate all sessions or perform a specific forensic procedure after upgrading. Those steps may be appropriate in an environment with its own indicators of compromise, but they should not be presented as official Mnemosyne remediation requirements without supporting guidance.
What operators should verify after upgrading
Confirm that the deployed server is actually running 3.10.1 or later and that the vulnerable endpoint is no longer exposed through an older instance, container or rollback. Keep the same canonical article under review for any advisory revision, confirmed exploitation, new fixed release, CISA KEV addition or project guidance that changes the required remediation.
Verification note: TPS reconciled the Mnemosyne project security information with the reviewed GitHub advisory, OSV record, GitLab advisory data and the published 3.10.1 package state. The affected-version boundary, fixed release and JWT verification failure are confirmed; exploitation prevalence remains unresolved.