






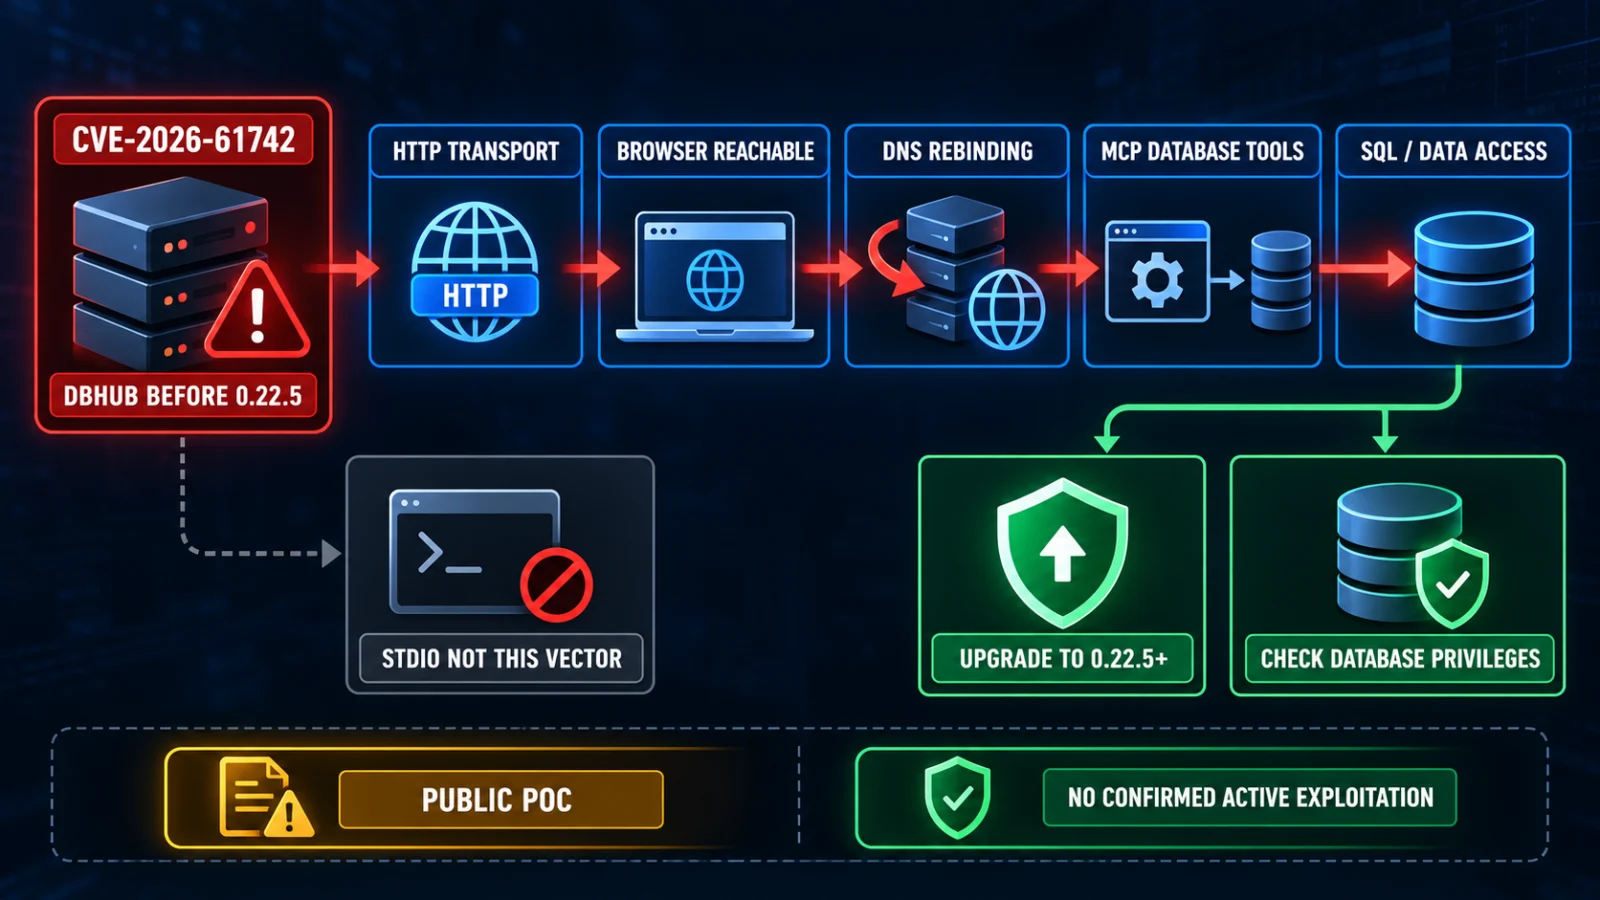
CVE-2026-61742 affects DBHub versions before 0.22.5 when the vulnerable HTTP MCP transport can be reached through a victim’s browser. GitHub’s reviewed advisory says DNS rebinding can let a malicious webpage reach DBHub and invoke MCP database tools without first supplying a DBHub authorization token. Version 0.22.5 contains the fix.
The vulnerability is serious because successful access can expose database operations such as schema enumeration, data reads and SQL execution. The actual impact still depends on which DBHub tools are enabled, what database credentials DBHub holds and whether the browser can reach the HTTP endpoint. TPS found a public proof of concept in the reviewed evidence, but no confirmed active exploitation.
CVE-2026-61742 affected versions and fixed version
| DBHub state | CVE-2026-61742 status | Reader action |
|---|---|---|
| Version before 0.22.5 using HTTP transport | Affected | Upgrade to 0.22.5 or later and review exposure |
| Version 0.22.5 or later | Fixed for this reported flaw | Confirm the deployed version and current advisory guidance |
| stdio transport | Not affected by this specific browser-origin DNS-rebinding vector | Do not assume other vulnerability classes are excluded |
Why HTTP transport matters
The attack depends on a browser being able to reach the DBHub HTTP service. In the vulnerable implementation, DBHub’s protection relied on comparing the browser’s Origin hostname with the request Host. DNS rebinding can defeat that assumption: an attacker-controlled hostname can initially resolve to the attacker’s infrastructure and later resolve to an address reachable from the victim’s browser while the hostname remains the same.
That makes an internal or locally reachable service relevant even when it is not intentionally published to the internet. Public internet exposure is therefore not the only exposure question. Administrators should determine whether browsers on developer or operator machines can reach the affected DBHub HTTP listener.
What successful exploitation can expose
GitHub’s advisory says the vulnerable HTTP path can permit unauthenticated MCP tool calls. Depending on the configured DBHub tools and database account permissions, an attacker could enumerate database structures, read information through exposed tools and invoke SQL execution functionality. Write impact is conditional: it depends on the privileges available to DBHub and the underlying database credentials.
The attack does not require prompt injection or compromise of an AI model. The browser itself is the path used to reach the DBHub service after DNS rebinding.
Is CVE-2026-61742 actively exploited?
No active in-the-wild exploitation was confirmed in the evidence reviewed by TPS. A reproducible public proof of concept exists, which establishes that the attack path can be demonstrated, but proof-of-concept availability must not be treated as evidence that attackers are already using the flaw against production systems. The reviewed CVE metadata also did not show CVE-2026-61742 in CISA’s Known Exploited Vulnerabilities catalog.
What DBHub administrators should check
Identify the deployed DBHub version. Versions before 0.22.5 are within the affected range documented by the reviewed advisory.
Determine whether the deployment uses HTTP transport. The specific browser-origin DNS-rebinding path described here does not apply to stdio.
Determine whether browsers on relevant workstations can connect to the DBHub HTTP endpoint, including local or internal addresses.
Move affected installations to version 0.22.5 or later and confirm that the running deployment actually uses the updated build.
Identify which databases, credentials and MCP tools the DBHub instance can access. These permissions determine the possible impact of successful exploitation.
If an affected HTTP service was reachable, review available DBHub, application and database records for unexpected MCP tool calls, SQL activity or unusual data access.
Additional hardening beyond the upgrade
The reviewed advisory recommends stronger controls around browser-reachable services, including restrictive host and origin policies, safer default binding and authentication or capability checks before sensitive MCP methods are dispatched. These controls reduce reliance on hostname equality as the only trust boundary.
Administrators should avoid assuming that a service is safe solely because it listens on a local or internal address. Browsers can act as a bridge to services that are unreachable directly from an external attacker’s network.
What remains unknown
TPS has not established active exploitation, the number of affected DBHub installations, the prevalence of HTTP transport in production or a definitive set of compromise indicators. There is also no evidence in the reviewed material showing how many exposed deployments use database credentials capable of modifying data.
This article should be updated on the same URL if GitHub, DBHub, CISA or another authoritative source confirms exploitation, changes the fixed-version guidance, publishes detection indicators or adds materially different hardening instructions.