






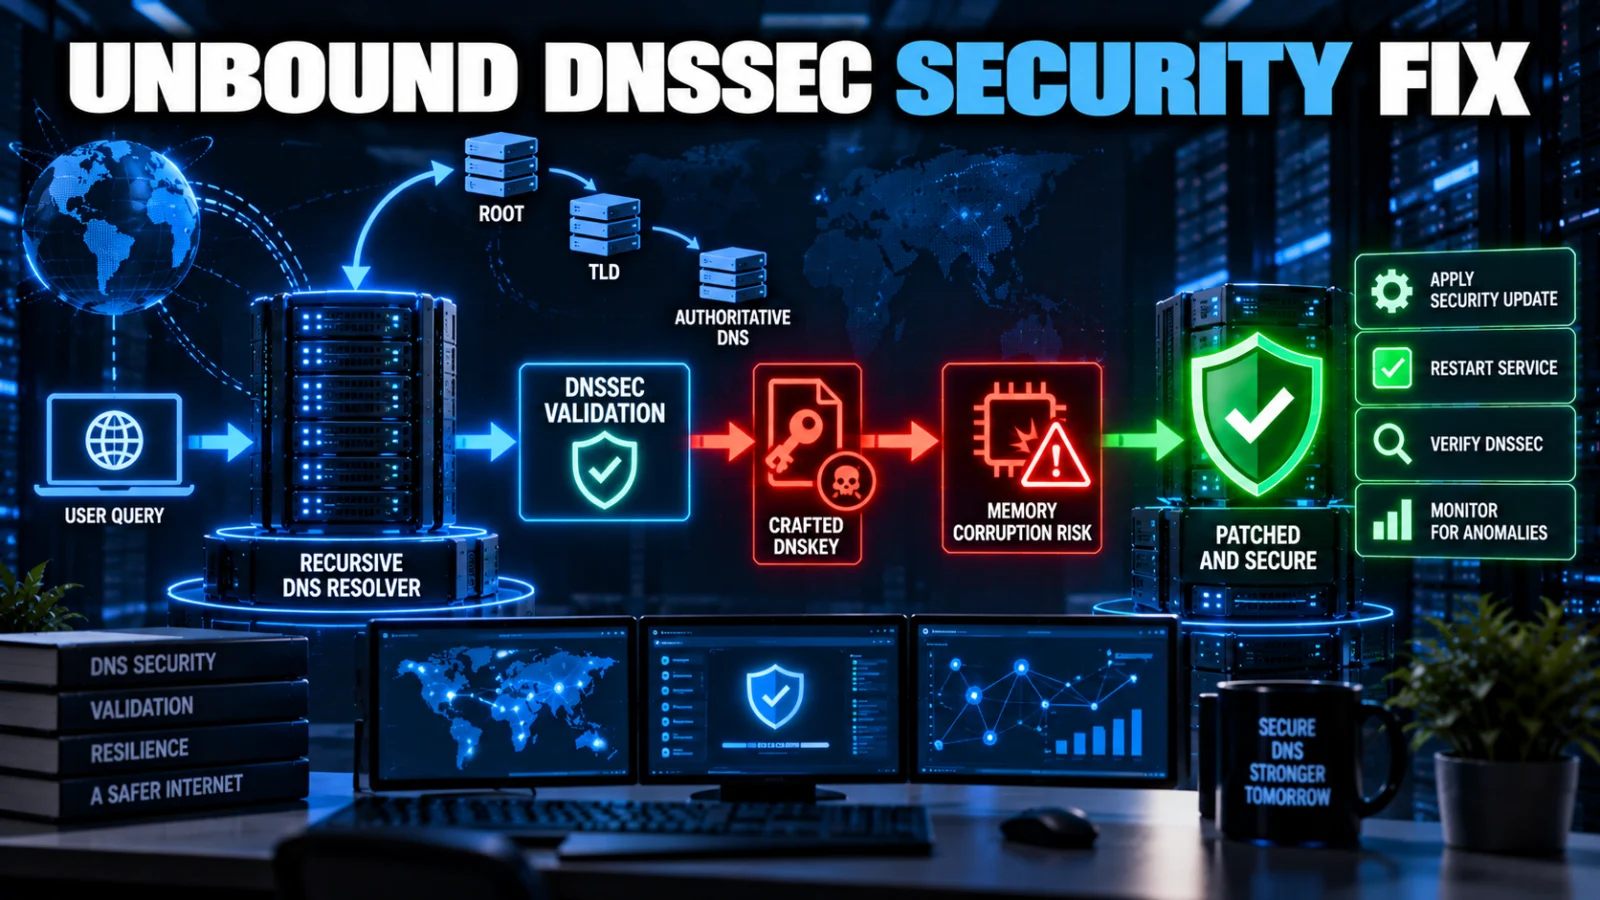
CVE-2026-81642 is a critical heap-buffer-overflow vulnerability in the Unbound DNSSEC validator. NLnet Labs says an attacker controlling a malicious DNS zone can craft DNSKEY data that causes memory corruption when a vulnerable resolver processes it. The confirmed impact includes denial of service, while the maintainer also says remote code execution is possible. Upstream Unbound versions through 1.26.0 are affected, and 1.26.1 contains the upstream fix.
The safest remediation depends on how Unbound is installed. Administrators using upstream or source builds should move to 1.26.1 or another later supported fixed release. Systems managed through Linux or BSD package repositories should follow the operating-system vendor’s security package guidance because distributions can backport the fix without using the same upstream version number.
CVE-2026-81642 affected and fixed versions
| Installation state | What the reviewed evidence says |
|---|---|
| Upstream Unbound 1.26.0 or earlier | Affected by CVE-2026-81642. |
| Upstream Unbound 1.26.1 | Contains the upstream fix. |
| Distribution-managed package | Check the distribution’s current CVE or security-advisory page because the patch may be backported into a package whose version does not match upstream 1.26.1 exactly. |
How the DNSSEC heap overflow is triggered
The vulnerability is in Unbound’s DNSSEC validation path rather than a generic DNS query-processing condition. According to NLnet Labs, a malicious zone can provide a crafted DNSKEY whose owner compression pointer points into its own RDATA. Processing that data can overflow the digest buffer and corrupt memory.
This means the flaw is remotely triggerable through DNS resolution, but the attack path still has an important prerequisite: the attacker controls a malicious DNS zone and causes the vulnerable resolver to process the crafted DNSSEC data. It would be inaccurate to describe the flaw simply as an arbitrary packet causing guaranteed remote code execution on every Unbound installation.
What does possible remote code execution mean?
NLnet Labs describes denial of service and possible remote code execution as potential consequences. TPS therefore preserves that wording. The vulnerability should not be presented as proven reliable code execution across all operating systems, builds or allocator configurations.
The security consequence is still serious even without confirmed reliable RCE. A remotely triggered heap overflow can crash a recursive resolver, disrupt DNS service and create a memory-corruption condition involving attacker-controlled input.
How to check whether your Unbound resolver needs action
Determine whether the resolver comes from an upstream/source build, an operating-system package or a downstream appliance or platform.
For upstream builds, versions through 1.26.0 are affected. For packaged systems, use the vendor’s CVE tracker or security advisory rather than comparing only the displayed upstream version.
Upgrade upstream builds to 1.26.1 or a later supported fixed release. For vendor packages, install the vendor-issued security update that incorporates the CVE-2026-81642 fix.
Distribution security trackers can change after disclosure, so verify the current package state before making production changes.
Current distribution package status reviewed by TPS
The package state was not uniform across the reviewed operating-system vendors. Debian’s tracker showed a fixed security package for Debian 13/trixie, while some older package rows remained vulnerable at the time of review. Ubuntu’s CVE page still showed supported releases as needing evaluation when TPS checked it. Amazon Linux had already published security advisories with fixed packages.
These differences are why administrators should not blindly replace a distribution-managed package with upstream 1.26.1. A distribution may deliver the same security correction as a backport while retaining a different package version.
What if an upstream upgrade cannot be completed immediately?
NLnet Labs provides source patches for the vulnerability in addition to the 1.26.1 release. Source-build operators who cannot immediately move releases should use the maintainer-provided patch appropriate to their build process rather than relying on an unverified network workaround. Distribution-managed systems should continue to follow their vendor’s supported security-update mechanism.
Is CVE-2026-81642 actively exploited?
TPS did not verify evidence during the completed review that CVE-2026-81642 is being actively exploited in the wild. The absence of verified exploitation evidence should not be treated as proof that exploitation is impossible. Operators should remediate based on the confirmed memory-corruption vulnerability and its possible code-execution impact rather than waiting for exploitation reports.
What could change next
This article should be updated if NLnet Labs changes the affected-version guidance, if more distributions publish fixed package states, if downstream products disclose bundled vulnerable Unbound versions, or if credible exploitation evidence or a CISA Known Exploited Vulnerabilities listing appears. Those changes would normally belong on this same URL while the core reader task remains exposure verification and remediation.