
CERT-In cyber threats 2026 data reported to Parliament shows 3,67,462 detected and mitigated malicious scanning, probing and vulnerable-service instances across banking and healthcare during January–June 2026. Banking accounted for 3,48,607 instances and healthcare for 18,855.
These figures describe detected cyber-threat activity, not a count of successful hacks, compromised bank accounts, breached hospitals or stolen patient records. The distinction matters because one organisation can generate many detections and a blocked probe can still appear in security-monitoring data.
Direct answer
The strongest signal is sustained hostile activity against important digital infrastructure. The H1 2026 totals show a substantial volume of scanning, probing and vulnerable-service exposure, but they do not establish an equivalent number of successful compromises.
Do not convert detections into victims
3,67,462 detections does not mean 3,67,462 organisations, accounts or patients were hacked.
What this analysis covers
5 Key CERT-In Cyber Threat Numbers for 2026
Detected and mitigated scanning, probing and vulnerable-service instances.
Detected and mitigated scanning, probing and vulnerable-service instances.
Banking and healthcare combined.
A narrower intrusion metric.
Full-year comparison for targeted campaigns.
Important: 3,67,462 is not a successful-hack count. Reporting attributes these figures to malicious scanning, probing and vulnerable services detected and mitigated by CERT-In.
What Do the Numbers Actually Measure?
Cyber monitoring can detect hostile activity before an attacker successfully compromises a target. Reported activity includes malicious scanning and probing as well as exposure involving vulnerable services.
For banking, the H1 2026 total of 3,48,607 includes 3,09,288 malicious scanning and probing instances and 39,319 vulnerable-service instances.
For healthcare, the H1 2026 total of 18,855 includes 18,259 malicious scanning and probing instances and 596 vulnerable-service instances.
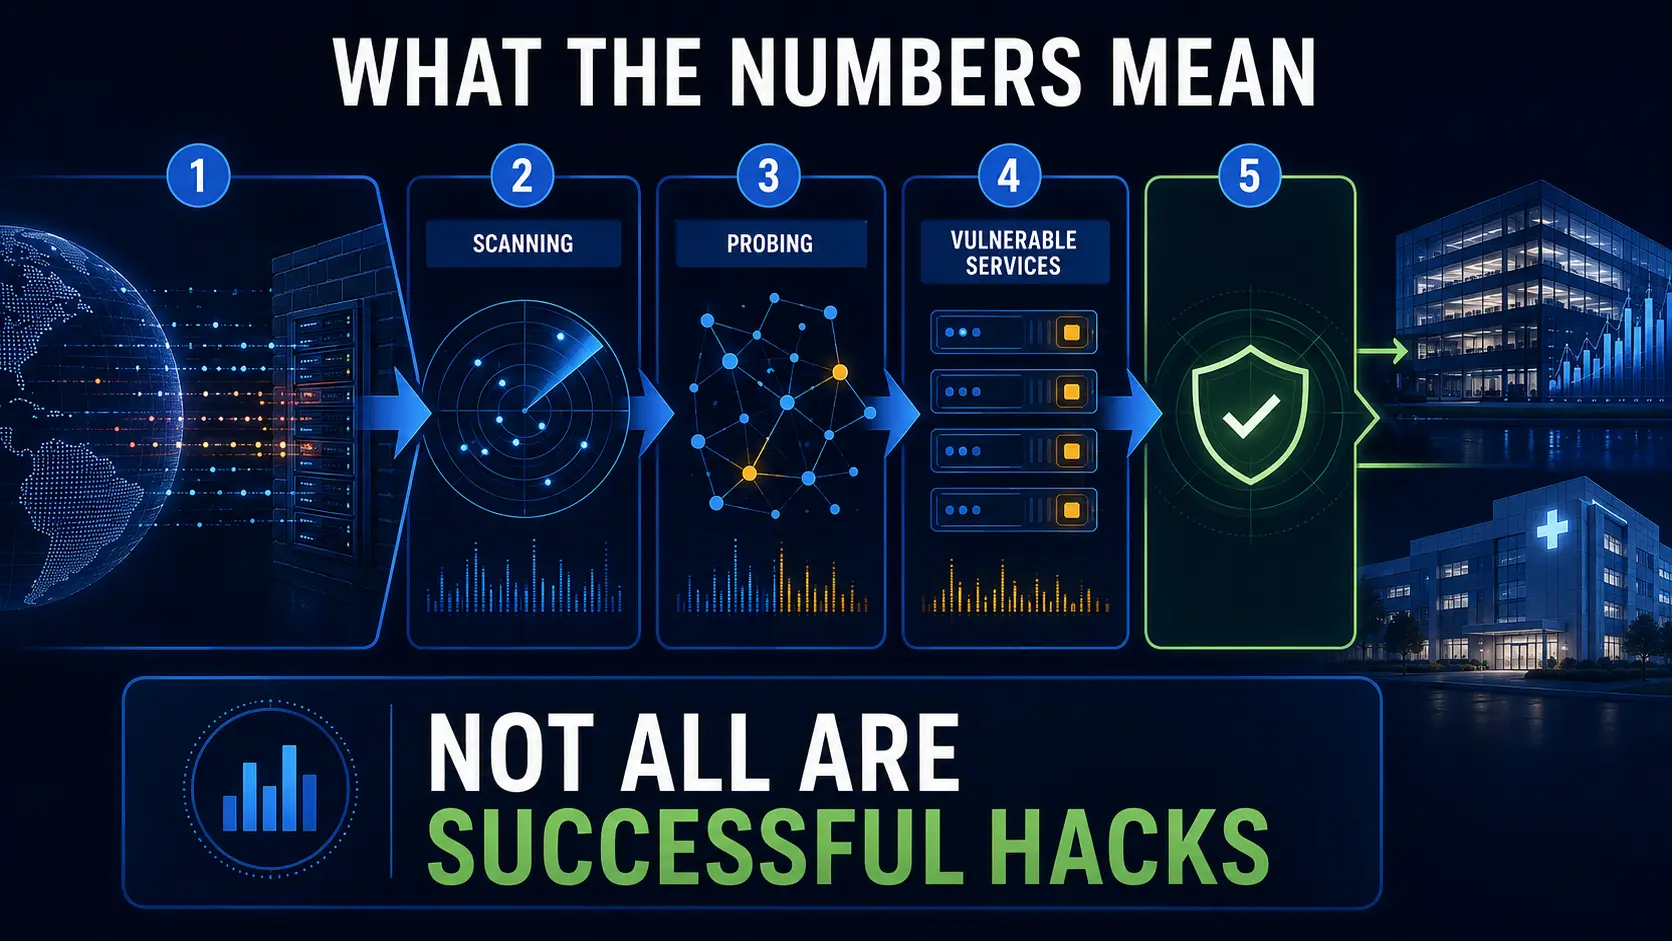
Detection ≠ successful compromise. Repeat probes, blocked attempts and repeated activity against the same infrastructure can all contribute to aggregate threat-monitoring counts.
Banking Sector: 3,48,607 H1 2026 Instances
The banking sector accounted for most of the combined H1 total. Reporting attributed 3,48,607 detected and mitigated instances to banking during January–June 2026.
For full-year 2025, the corresponding banking total was 5,70,108.
The H1 2026 figure is therefore about 61% of the full-year 2025 banking total, but that comparison should not be treated as a forecast for the second half of 2026.
3,48,607 banking detections does not mean 3,48,607 bank accounts were hacked. The data describes monitored hostile activity against banking infrastructure rather than customer-account compromise.
Healthcare Sector: 18,855 H1 2026 Instances
CERT-In-linked data reported for healthcare shows 18,855 detected and mitigated instances in the first half of 2026, compared with 34,480 in full-year 2025.
The H1 2026 healthcare total includes 18,259 malicious scanning and probing detections and 596 vulnerable-service detections.
The defensible interpretation: healthcare infrastructure is experiencing persistent hostile and vulnerability-focused activity. The aggregate number does not establish how many hospitals, systems or patients experienced a successful breach.
What Does the H1 2026 vs 2025 Comparison Show?
Banking and healthcare together recorded 6,04,588 relevant instances during full-year 2025 and 3,67,462 during January–June 2026.
The first-half 2026 total is about 60.8% of the entire 2025 total. That supports the conclusion that hostile activity remained elevated, but it does not prove the full-year 2026 figure will be twice the first-half total.
Do not annualise H1 automatically. Cyber-threat activity can change significantly over the remainder of the year.
Why Are Targeted Bank Intrusion Campaigns a Separate Metric?
CERT-In also detected and mitigated 17 targeted intrusion campaigns involving the banking sector in H1 2026, compared with 39 in all of 2025.
This is a much narrower category than broad scanning, probing and vulnerable-service detections, so the two metrics should not be combined or compared as if they measure the same thing.
| Metric | H1 2026 | What it represents |
|---|---|---|
| Banking threat detections | 3,48,607 | Broad scanning, probing and vulnerable-service activity. |
| Healthcare threat detections | 18,855 | Broad scanning, probing and vulnerable-service activity. |
| Targeted bank intrusion campaigns | 17 | A narrower targeted-intrusion category. |
Apple Users: A Newer Critical CERT-In Advisory Includes macOS Tahoe
CERT-In advisory CIAD-2026-0041 identifies critical vulnerabilities affecting Apple products, including macOS Tahoe versions prior to 26.6.2. The advisory also covers affected iOS and iPadOS versions and warns that successful exploitation could enable arbitrary code execution, sensitive-information exposure, security-boundary compromise or denial-of-service conditions.
This is separate from CERT-In vulnerability note CIVN-2026-0398 issued on August 10 for the macOS Screen Sharing authentication-bypass flaw. That earlier note listed Sonoma versions before 14.8.9, Sequoia versions before 15.7.9 and Tahoe versions before 26.6.1 as affected by the Screen Sharing issue.
CERT-In advises users to apply the appropriate vendor security updates. Neither advisory proves that every affected Apple device has been exploited or compromised.
Install the latest supported Apple security update offered for the device. Do not stop at an older minimum version if Apple offers a newer supported security release.
What Should Bank Customers, Healthcare Users and Apple Users Do?
Bank customers
Use official banking channels, protect OTPs and authentication codes, review unexpected transactions and report suspicious activity promptly.
Healthcare users
Do not assume your records were exposed from a national threat count alone. Follow provider-specific guidance if your hospital or service announces an incident.
Apple users
Check Software Update on the device and install the latest supported security release offered by Apple rather than relying only on an older minimum-version threshold.
Organisations
Maintain patching, exposure management, monitoring and incident-response processes rather than treating aggregate threat counts as an individual compromise diagnosis.
What the Current Evidence Does Not Prove
- It does not prove 3,67,462 successful hacks.
- It does not prove 3,48,607 bank accounts were compromised.
- It does not prove 18,855 healthcare organisations were breached.
- It does not establish a unique victim count.
- It does not establish how many attempts caused financial loss or data theft.
- It does not prove H2 2026 will continue at the same rate.
- The Apple advisories do not prove widespread exploitation of every affected device in India.
Verification Method
Evidence checked
Times of India and Outlook Money reporting was cross-checked for the banking and healthcare figures attributed to CERT-In data supplied to Parliament. Both report the same H1 2026 totals: 3,48,607 for banking, 18,855 for healthcare and 3,67,462 combined.
CERT-In advisory CIAD-2026-0041 was checked for the newer Apple security state. It lists macOS Tahoe versions prior to 26.6.2 among affected Apple products and recommends applying vendor updates. CERT-In vulnerability note CIVN-2026-0398 was also rechecked as the earlier, narrower macOS Screen Sharing authentication-bypass notice.
PIB material was checked for CERT-In’s broader national incident-response role and current cybersecurity preparedness context.
Sources
- CERT-In — CIAD-2026-0041 Multiple Vulnerabilities in Apple Products
- CERT-In — CIVN-2026-0398 macOS Screen Sharing authentication bypass
- Times of India — parliamentary banking and healthcare figures
- Outlook Money — parliamentary banking and healthcare figures
- PIB — CERT-In national cyber-security incident context
Limitations and Unresolved Facts
- The exact Rajya Sabha question-and-answer document containing the banking and healthcare table was not located during this review, so the numerical sector table remains corroborated through multiple reports explicitly attributing it to Government/CERT-In data supplied to Parliament.
- The aggregate threat figures do not provide unique organisation, account, patient or victim counts.
- The data does not establish how repeated scanning or probing is deduplicated.
- The sector figures do not establish how many detections resulted in successful compromise, fraud, data theft or financial loss.
- CERT-In’s August 19 Apple advisory describes critical vulnerabilities and affected version boundaries but does not establish that every affected Apple device has been exploited.
CERT-In Cyber Threats 2026 FAQs
What is the correct H1 2026 banking figure?
The reported CERT-In-linked total is 3,48,607 detected and mitigated malicious scanning, probing and vulnerable-service instances.
What is the correct healthcare figure?
18,855 instances for January–June 2026.
What is the combined total?
3,67,462 banking and healthcare instances in H1 2026.
Does that mean 3.67 lakh successful hacks?
No. The figures cover detected and mitigated scanning, probing and vulnerable-service activity and should not be converted into a successful-hack count.
How many targeted bank intrusion campaigns were reported?
17 in H1 2026, compared with 39 during full-year 2025.
What is the current CERT-In Apple warning covered here?
CERT-In advisory CIAD-2026-0041, issued August 19, covers multiple critical vulnerabilities in Apple products and lists macOS Tahoe versions before 26.6.2 among the affected software. Users should install the latest supported Apple security update offered for their device.
Last verified: September 15, 2026.