






CVE-2026-94127 is a critical F5 BIG-IP Access Policy Manager vulnerability that F5 says is being exploited in the wild. The flaw can allow unauthenticated remote code execution, but exposure is configuration-specific: the affected virtual server must have both an APM access policy and an OAuth profile, with APM operating as the OAuth Authorization Server.
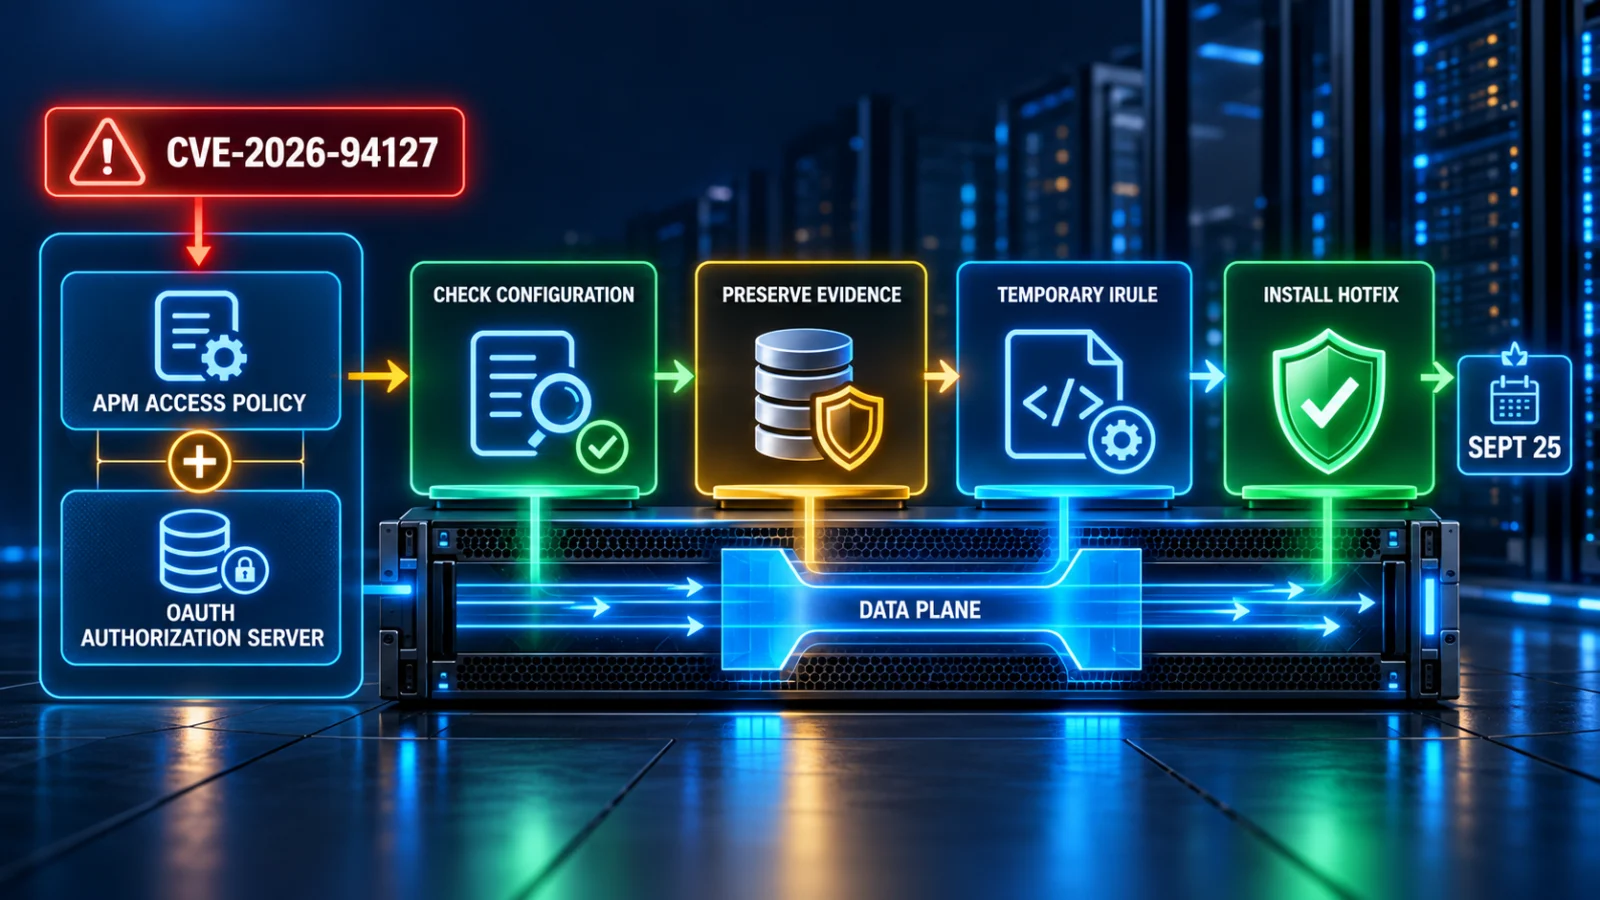
Direct answer: administrators should first verify whether their BIG-IP APM deployment matches the affected OAuth authorization-server configuration. If it does, preserve relevant forensic evidence when compromise is suspected, use F5’s vendor-provided temporary iRule if immediate patching is not possible, and install the engineering hotfix for the exact supported BIG-IP branch. OAuth Client-only and OAuth Resource Server-only deployments are not affected by this CVE according to F5’s published scope.
What changed with CVE-2026-94127?
F5 disclosed CVE-2026-94127 on September 22, 2026 and reported that the vulnerability had already been exploited. CISA subsequently added it to the Known Exploited Vulnerabilities catalog and assigned a September 25 remediation date for the applicable federal scope.
This changes the reader problem from routine vulnerability review to immediate exposure verification and remediation. The issue is rated 9.8 Critical under CVSS v3.1 and 9.3 Critical under CVSS v4.0.
Which BIG-IP APM configuration is vulnerable?
BIG-IP APM is not automatically vulnerable merely because the module is provisioned. F5’s affected condition requires an APM access policy and an OAuth profile on the same virtual server, with APM functioning as an OAuth Authorization Server.
| Configuration | CVE-2026-94127 status |
|---|---|
| APM access policy + OAuth Authorization Server profile on the same virtual server | Affected configuration |
| APM used strictly as OAuth Client | Not affected by this CVE |
| APM used strictly as OAuth Resource Server | Not affected by this CVE |
| End-of-Technical-Support software | Not evaluated by F5; do not assume unaffected |
How serious is the F5 BIG-IP APM flaw?
F5 describes CVE-2026-94127 as a heap-based buffer overflow. An unauthenticated attacker with network access to an affected virtual server can send malicious traffic and potentially execute code.
The CVSS v3.1 vector is network reachable, requires low attack complexity, requires no privileges and no user interaction, and carries high confidentiality, integrity and availability impact.
The combination of pre-authentication network access and confirmed exploitation is why CISA’s KEV status matters beyond the numerical severity score.
Is this a BIG-IP management-interface vulnerability?
No. F5 describes CVE-2026-94127 as a data-plane vulnerability rather than a management or control-plane issue.
Restricting the administrative management interface is still good security practice, but it does not remediate this vulnerability when the affected OAuth authorization-server virtual server remains reachable.
F5 also states that BIG-IP Appliance mode does not remove the exposure.
CVE-2026-94127 hotfixes by BIG-IP branch
F5 has issued engineering hotfixes for the supported affected branches identified in the completed advisory review. Administrators should verify the exact installed software branch before selecting a hotfix.
| Affected BIG-IP branch | Engineering hotfix |
|---|---|
| 21.1.0 | Hotfix-BIGIP-21.1.0.2.0.30.22-ENG or later |
| 17.5.0–17.5.1 | Hotfix-BIGIP-17.5.1.9.0.160.12-ENG or later |
| 17.1.0–17.1.3 | Hotfix-BIGIP-17.1.3.5.0.41.14-ENG or later |
Software versions that have reached End of Technical Support were not evaluated by F5. Their absence from the supported-version table must therefore not be interpreted as confirmation that they are safe.
What administrators should do now
Identify virtual servers that combine an APM access policy with an OAuth profile and determine whether APM is functioning as the OAuth Authorization Server.
Collect and preserve relevant forensic evidence before disruptive remediation where operationally feasible. Patching should not be treated as proof that an already-vulnerable system was never exploited.
If the hotfix cannot be installed immediately, obtain F5’s vendor-provided iRule mitigation through F5 Support. Do not recreate or improvise the rule from unofficial sources.
Apply the engineering hotfix that matches the supported BIG-IP branch, then continue incident investigation if there are signs the device may already have been compromised.
Is the iRule mitigation a permanent fix?
No. The iRule is a temporary mitigation intended to reduce exposure and support forensic triage when immediate patching is not possible. It does not replace the final vendor remediation.
Administrators should obtain the rule from F5 Support and then move to the appropriate engineering hotfix as soon as operationally possible.
Why preserve forensic evidence before patching?
F5 says the flaw has already been exploited. If an affected system has suspicious activity, immediately modifying or rebooting it may destroy evidence useful for determining whether compromise occurred and what an attacker did afterward.
CERT-EU therefore recommends preserving relevant forensic evidence before remediation where feasible. This does not mean delaying protection indefinitely; it means treating exposure verification, evidence preservation and patching as parts of the same incident-response sequence.
What does the September 25 CISA deadline mean?
CISA’s KEV entry lists September 25, 2026 as the remediation due date for the applicable U.S. federal scope.
The date is not a universal legal deadline for every private organization. However, non-federal organizations should still treat KEV inclusion as strong evidence that remediation deserves immediate priority because active exploitation is confirmed and vendor fixes are available.
Is ransomware using CVE-2026-94127?
CISA’s current KEV record lists known ransomware-campaign use as Unknown. TPS did not establish a confirmed ransomware group, named attacker or campaign tied to this CVE in the completed research.
Active exploitation is confirmed; ransomware attribution is not.
Is public exploit code available?
A publicly available proof of concept was not confirmed in the reviewed evidence. That status can change quickly after disclosure, so the absence of a confirmed public PoC should not be treated as a reason to delay remediation when exploitation is already known to occur.
What remains unknown about the exploitation?
The reviewed evidence does not establish the threat actor, victim count, first exploitation date, geographic scope, whether attacks are broadly automated or targeted, what post-exploitation tooling is used, whether persistence is being established, or whether credentials or configuration data have been stolen in observed incidents.
F5 may publish additional indicators, threat-hunting guidance or exploitation details. Any material change should update this same CVE-2026-94127 canonical.
What happens next?
The nearest verified state transition is the September 25 CISA remediation milestone. Beyond that, administrators should watch for revised F5 guidance, general-availability maintenance releases containing the fix, new engineering hotfixes, public indicators of compromise, threat-actor attribution, ransomware-status changes and any expansion of the affected configuration or software scope.
Verification note
TPS reconciled F5’s vulnerability scope and remediation information with CISA KEV status, the Canadian Centre for Cyber Security advisory, CERT-EU guidance and current independent security analysis. The exposure condition, active exploitation state and supported engineering hotfixes are confirmed. Attacker identity, victim scope, ransomware use, public exploit availability, end-of-support exposure and full post-exploitation behavior remain unresolved.