






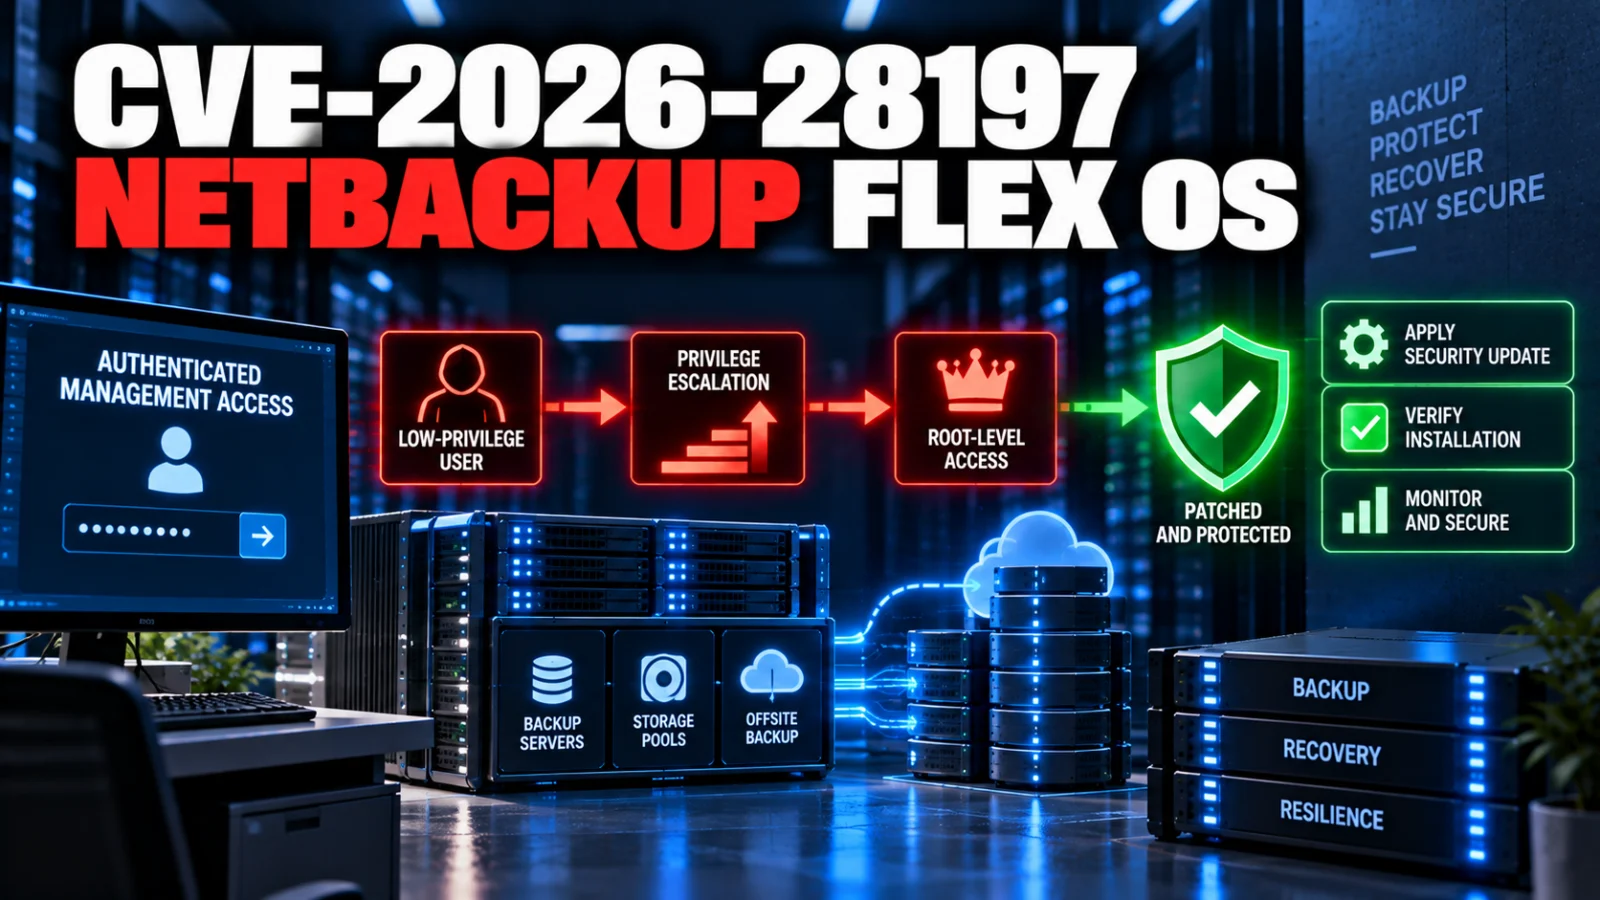
CVE-2026-28197 NetBackup Flex OS affects NetBackup Flex OS versions earlier than 6.4. According to Cohesity’s security advisory, an authenticated user with low-privileged access to the Flex OS management shell can exploit an argument-injection flaw to execute arbitrary code with root privileges. Cohesity’s remediation is to upgrade affected systems to Flex OS 6.4 or later.
The important boundary is authentication. This is not described by the vendor as an unauthenticated or pre-authentication compromise. An attacker must already have access to a low-privileged management-shell account. That prerequisite reduces the attack surface compared with a pre-authentication flaw, but the impact after successful exploitation is still severe because the resulting code execution runs with root-level permissions.
CVE-2026-28197 NetBackup Flex OS affected versions
Cohesity identifies NetBackup Flex OS releases earlier than version 6.4 as affected. Administrators should therefore begin by confirming the exact Flex OS version running on each appliance. Systems already running 6.4 or a later release are outside the affected version range described in the reviewed advisory.
For environments below 6.4, the version check should not stop at identifying exposure. The vendor’s guidance treats upgrading as the required remediation rather than relying only on access restrictions.
What an attacker needs
The vulnerability requires an authenticated user with low-privileged access to the NetBackup Flex OS management shell. The flaw is described as argument injection: specially crafted input can cause commands to be executed with privileges beyond those normally granted to that user.
If exploitation succeeds, the user can execute arbitrary code with root permissions. That can provide unrestricted control over the Flex host and the containers hosted on it, making the privilege boundary the central security issue for affected administrators.
What administrators should do
- Confirm the installed Flex OS version. Treat releases earlier than 6.4 as affected according to the reviewed vendor advisory.
- Restrict management-shell access. Until remediation is complete, keep shell access limited to authorized administrators and remove unnecessary low-privileged shell access.
- Upgrade to Flex OS 6.4 or later. Cohesity identifies upgrading as the remediation for CVE-2026-28197.
- Do not treat access restriction as the final fix. The vendor states that no compensating control fully eliminates the vulnerability risk for affected versions.
Does restricting the management shell fully fix the issue?
No. Restricting management-shell access reduces who can reach the vulnerable path and is a useful interim risk-reduction measure, but Cohesity does not present it as a complete remediation. The security boundary remains vulnerable on affected releases until the system is upgraded.
Is CVE-2026-28197 actively exploited?
The reviewed evidence does not establish active exploitation in the wild. TPS therefore does not describe CVE-2026-28197 as actively exploited, a zero-day or a pre-authentication remote-code-execution vulnerability. That status could change if Cohesity, CISA or another authoritative source later publishes new exploitation evidence.
What changed
The vulnerability is now publicly identifiable under CVE-2026-28197 with an affected-version boundary, attacker prerequisite and remediation path that administrators can act on. The practical answer is straightforward: if a NetBackup Flex OS deployment is earlier than 6.4, confirm who has management-shell access, restrict that access while remediation is underway, and upgrade to 6.4 or later.
What TPS will watch next
ThePulseSignal will treat any later Cohesity advisory revision, confirmed exploitation, CISA Known Exploited Vulnerabilities addition, changed affected-version range or new remediation guidance as a material update to this same article rather than creating a duplicate URL for the same reader problem.