






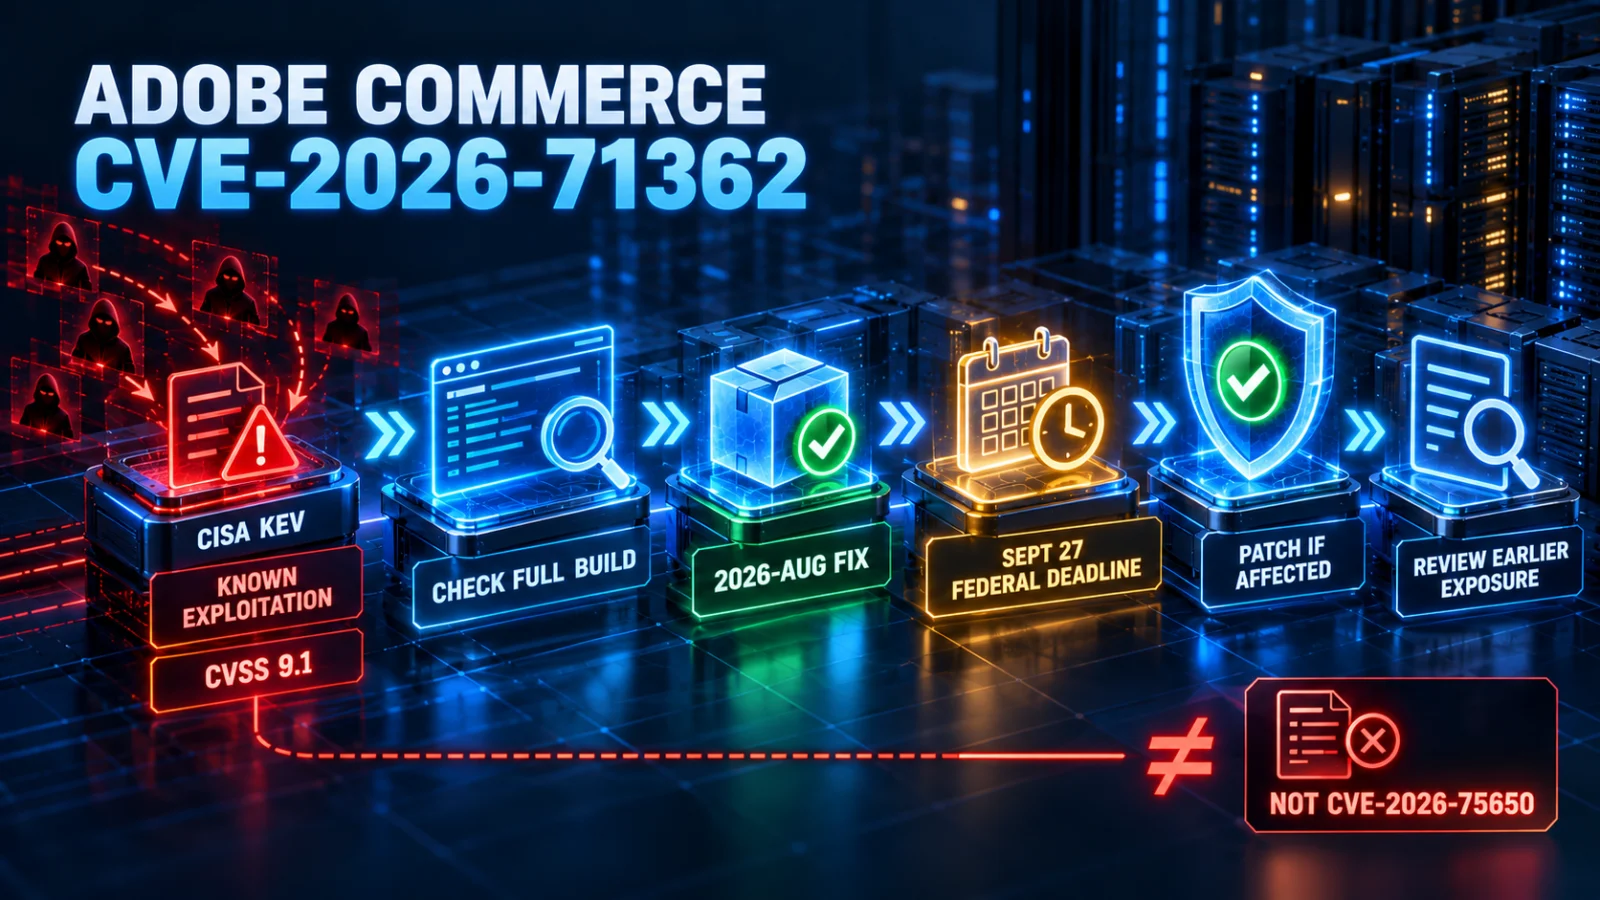
CISA added Adobe Commerce CVE-2026-71362 to its Known Exploited Vulnerabilities catalog on September 24, 2026, confirming that the authorization flaw has been exploited in the wild. Adobe had already patched the issue in its August Commerce and Magento security releases. CISA lists a September 27 remediation due date for covered federal systems, while private organizations should treat the KEV addition as a strong reason to verify their patch level immediately.
What changed for Adobe Commerce CVE-2026-71362?
The vulnerability itself is not newly disclosed. Adobe published its fix in August. What changed on September 24 is the exploitation state: CISA added CVE-2026-71362 to KEV, moving the current answer from researcher-reported exploitation to a government-confirmed known-exploited state.
The flaw is an incorrect authorization vulnerability affecting Adobe Commerce and Magento. Adobe scores it 9.1 Critical. Its CVSS vector requires no privileges and no user interaction.
What can CVE-2026-71362 allow?
Adobe classifies CVE-2026-71362 as CWE-863, Incorrect Authorization. Successful exploitation can provide elevated access to sensitive resources that the attacker should not normally be able to reach.
This distinction matters: CVE-2026-71362 is not documented by Adobe as a remote-code-execution vulnerability. TPS therefore does not describe it as RCE.
Is CVE-2026-71362 actively exploited?
Yes. CISA’s KEV listing now establishes that the vulnerability has been exploited in the wild.
That current state is stronger than Adobe’s original August bulletin, which said at publication time that Adobe was not aware of exploitation in the wild. That historical statement described what Adobe knew then; it does not override CISA’s September 24 KEV determination.
Before the KEV addition, security researchers and current security reporting had already described exploitation attempts. Research cited by current coverage said attackers could abuse the authorization flaw to switch customer-session context and reach information belonging to another account. TPS treats that specific attack behavior as researcher-reported rather than wording directly confirmed in Adobe’s advisory.
Which Adobe Commerce builds contain the fix?
Adobe’s CVE data marks the corresponding August 2026 security patch levels as unaffected. Administrators should compare the complete installed build string, not only the base 2.4.x version.
| Product branch | Fixed / unaffected August build |
|---|---|
| Adobe Commerce 2.4.9 | 2.4.9-2026-aug |
| Adobe Commerce 2.4.8 | 2.4.8-2026-aug |
| Adobe Commerce 2.4.7 | 2.4.7-2026-aug |
| Adobe Commerce 2.4.6 | 2.4.6-2026-aug |
| Adobe Commerce 2.4.5 | 2.4.5-2026-aug |
| Adobe Commerce 2.4.4 | 2.4.4-2026-aug |
Adobe’s vulnerability data identifies earlier patch levels in those branches as affected. The exact dated patch suffix therefore matters when checking exposure.
Which Adobe Commerce B2B builds contain the fix?
| Adobe Commerce B2B branch | Fixed / unaffected August build |
|---|---|
| 1.5.3 | 1.5.3-2026-aug |
| 1.5.2 | 1.5.2-2026-aug |
| 1.4.2 | 1.4.2-2026-aug |
| 1.3.4 | 1.3.4-2026-aug |
| 1.3.3 | 1.3.3-2026-aug |
Which Magento Open Source builds are fixed?
| Magento Open Source branch | Fixed / unaffected August build |
|---|---|
| 2.4.9 | 2.4.9-2026-aug |
| 2.4.8 | 2.4.8-2026-aug |
| 2.4.7 | 2.4.7-2026-aug |
| 2.4.6 | 2.4.6-2026-aug |
Does the September 27 CISA deadline apply to every company?
No. September 27, 2026 is the remediation due date CISA records for covered federal environments under its vulnerability-remediation framework. TPS does not treat that date as a universal legal deadline for every private merchant or ecommerce operator.
The KEV designation is still highly relevant outside government because it establishes known exploitation. Private organizations running affected Commerce or Magento builds should therefore prioritize Adobe’s remediation even when the federal deadline does not directly govern them.
What should Adobe Commerce and Magento administrators do?
Check the full installed build
Verify the complete Adobe Commerce or Magento version and dated patch suffix. A base 2.4.x version alone is not enough to establish patch status.
Compare it with Adobe’s August fix
Confirm that the installed build is at the corresponding fixed August 2026 patch level or a later vendor-supported release containing the fix.
Apply the vendor remediation
If the environment remains on an affected build, follow Adobe APSB26-92 and current Adobe guidance rather than relying only on compensating controls.
Review earlier exposure
Because exploitation occurred before the KEV addition, systems that remained vulnerable may warrant defensive review for unexpected account or session activity and unauthorized changes.
Keep the two Adobe Commerce CVEs separate
CVE-2026-71362 and CVE-2026-75650 are different flaws with different advisories and remediation paths. Verify both independently where relevant.
Preserve evidence when compromise is suspected
Use normal incident-response procedures to preserve relevant application, access, authentication and administrative-change evidence before making destructive cleanup changes.
Is CVE-2026-71362 the same as CVE-2026-75650?
No. CVE-2026-75650 is a separate Adobe Commerce vulnerability disclosed in September and associated with a different Adobe advisory and emergency remediation. CVE-2026-71362 is the August incorrect-authorization flaw now added to CISA KEV.
The two issues should not be merged merely because both affect Adobe Commerce and have exploitation concerns.
Does CISA say ransomware is using CVE-2026-71362?
No confirmed ransomware linkage was established in the reviewed evidence. CISA’s current KEV data records known ransomware campaign use as Unknown.
TPS therefore does not attribute this vulnerability to ransomware crews or any specific threat actor without stronger evidence.
How many Adobe Commerce stores have been compromised?
No reliable total victim count was established in the reviewed evidence. CISA’s KEV listing confirms exploitation, but it does not establish that every vulnerable Adobe Commerce or Magento installation has been compromised.
TPS also did not verify named victims, a definitive campaign geography or a confirmed threat-actor attribution.
Adobe Commerce CVE-2026-71362: current evidence state
| Question | Current state |
|---|---|
| Is CVE-2026-71362 in CISA KEV? | Yes |
| Is exploitation confirmed? | Yes, through CISA KEV |
| Does exploitation require privileges? | No |
| Does it require user interaction? | No |
| Is the Adobe CVSS score critical? | Yes, 9.1 |
| Is CVE-2026-71362 an Adobe-documented RCE flaw? | No |
| Is the September 27 deadline universal for private companies? | No |
| Is ransomware use confirmed? | Unknown |
| Is the total victim count known? | No reliable count established |
Adobe Commerce CVE-2026-71362: direct answers
What changed on September 24?
CISA added CVE-2026-71362 to the Known Exploited Vulnerabilities catalog, establishing a known-exploited state.
Was a patch already available?
Yes. Adobe had already addressed the vulnerability in its August 2026 security update.
What should administrators verify first?
The complete Commerce or Magento build and dated patch suffix should be checked against Adobe’s fixed August release for that product branch.
Should a patched store assume there was no earlier compromise?
No. Patching closes the vulnerability but does not prove that a previously exposed system was never abused. Where exposure overlapped known exploitation, a defensive compromise review may be warranted.
What could materially change this article?
An Adobe advisory revision, new CISA guidance, confirmed victims, campaign attribution, ransomware linkage, reliable compromise indicators, new patch guidance or evidence that the affected-version boundary changed would materially update the current answer.
Verification method
ThePulseSignal reviewed the CISA KEV addition, Adobe’s APSB26-92 security guidance and Adobe vulnerability data, then reconciled those primary sources with government and current security reporting about the earlier exploitation state.
Limitations
The reviewed evidence does not establish a reliable victim count, attacker attribution, ransomware linkage, current attack volume, campaign geography, persistence methods or the percentage of Adobe Commerce and Magento installations still running affected patch levels. Adobe’s original bulletin also predates the later CISA KEV confirmation.