






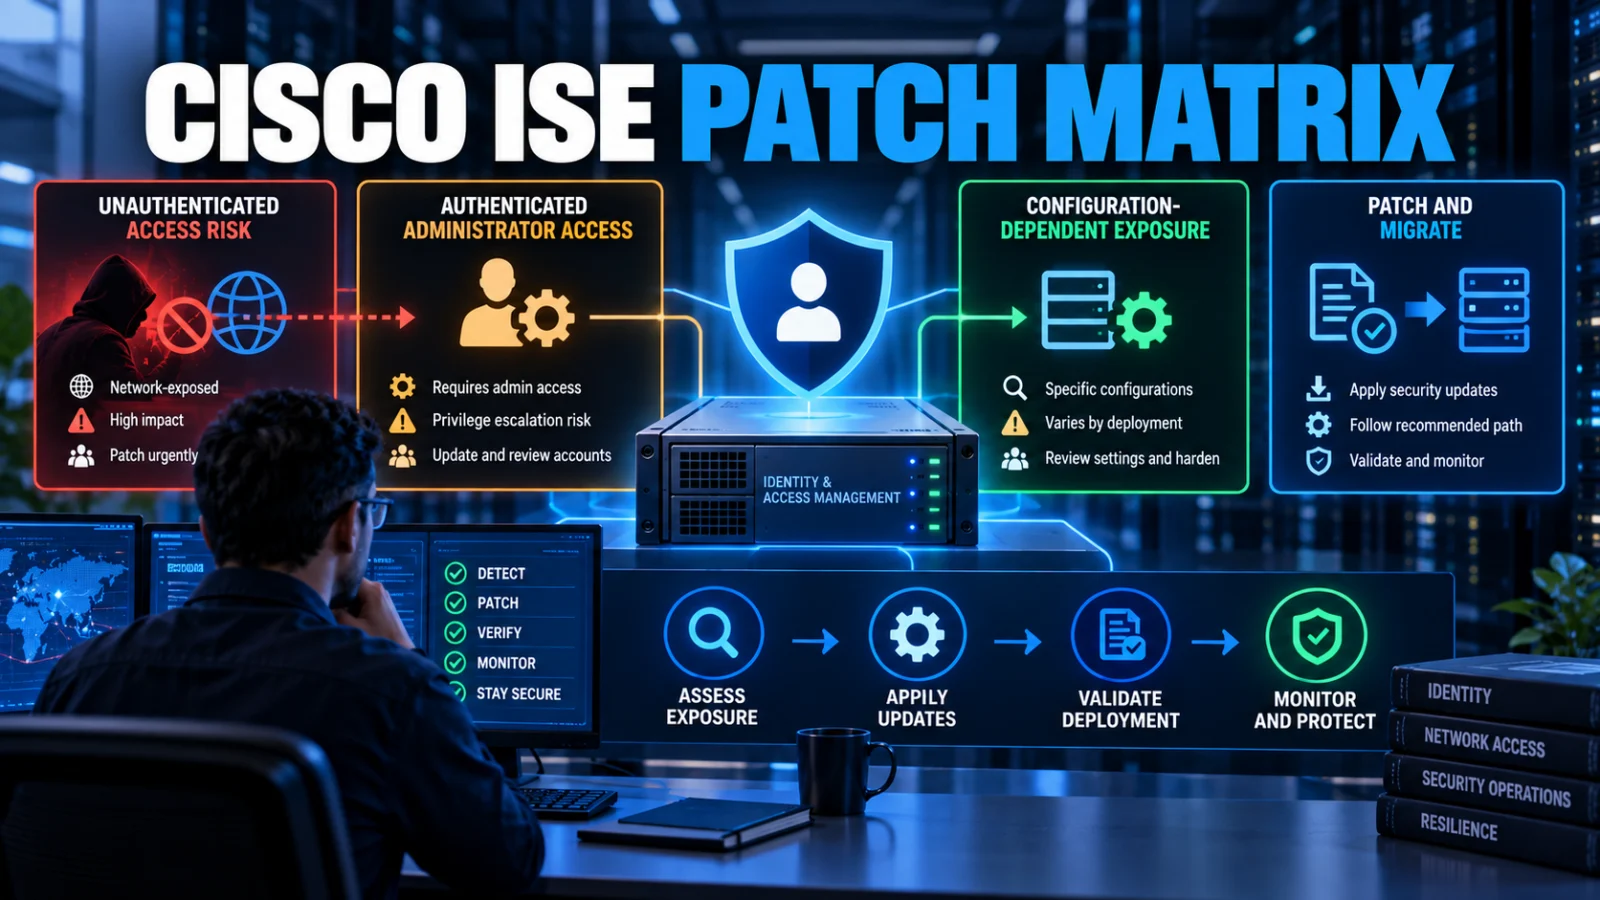
Cisco ISE September 2026 critical security updates should not be treated as one uniform vulnerability batch. Cisco published multiple ISE and ISE-PIC advisories on September 16, including Critical flaws, but the authentication requirements, configuration prerequisites, affected products, workarounds and first fixed releases differ by advisory and sometimes by individual CVE.
For many of the Critical September advisories, Cisco’s current fixed-release path converges on ISE 3.3 Patch 12, ISE 3.4 Patch 7 and ISE 3.5 Patch 4. Older 3.1 and 3.2 deployments may have a fixed patch for some CVEs but require migration for others. Administrators therefore need to map each advisory against the exact product, release, patch level and enabled configuration before deciding what to install.
Cisco ISE September 2026 critical security updates: patch matrix
| Advisory | Key CVEs | Max CVSS | Authentication or prerequisite | ISE-PIC | Workaround | Exploitation state | Patch direction |
|---|---|---|---|---|---|---|---|
| ISE Hardening Release | CVE-2026-20130, 20192, 20194, 20234, 20237, 20287 | 10.0 | Multiple vulnerability classes; Cisco’s advisory must be checked for each CVE | Yes | None | Do not transfer the separate CVE-2026-76460 exploitation state to this entire set | 3.1 Patch 12; 3.2 Patch 11; 3.3 Patch 12; 3.4 Patch 7; 3.5 Patch 4, with older releases requiring migration |
| ISE Multiple Vulnerabilities advisory | CVE-2026-76423 through CVE-2026-76428 | 10.0 | Mixed remote attack classes; applicability differs by CVE | Mixed | None | Cisco PSIRT did not report malicious use for this advisory in the reviewed state | CVE-specific; 3.3 Patch 12, 3.4 Patch 7 and 3.5 Patch 4 are key current fixed destinations, while some older releases require migration |
| Authentication Bypass | CVE-2026-76460 | 10.0 | Unauthenticated remote attack path | ISE | None | Known active exploitation according to Cisco’s related advisory state | Keep this CVE as a separate urgent incident-response and patching job rather than flattening it into the general batch |
| Remote Code Execution | CVE-2026-20176, 20211, 20307 | 9.9 | Valid administrative credentials required | ISE | None | Cisco PSIRT did not report malicious use in the reviewed advisory state | Per-CVE fixed releases differ; 3.3 Patch 12 and 3.4 Patch 7 are key destinations, while 3.5 fixes differ by CVE |
| Authenticated RCE and API vulnerabilities | CVE-2026-20282, 20283, 20284 | 9.1 | CVE-2026-20282 is configuration-independent; CVE-2026-20283 depends on the specified IPsec state; CVE-2026-20284 requires SXP to be enabled with an SXP connection | No | Available only for CVE-2026-20283 | Public announcement exists; Cisco said it was not aware of malicious use in the reviewed advisory state | 3.3 Patch 12; 3.4 Patch 7; 3.5 Patch 4, with CVE-specific treatment on older releases |
| Command Injection | CVE-2026-20305, 20306 | 9.1 | Valid administrative credentials required | Yes | None | Cisco PSIRT did not report malicious use in the reviewed advisory state | CVE-2026-20305 follows the newer patch baseline; CVE-2026-20306 has narrower release and patch-state applicability that must be checked separately |
Do not assume every Cisco ISE Critical flaw is unauthenticated
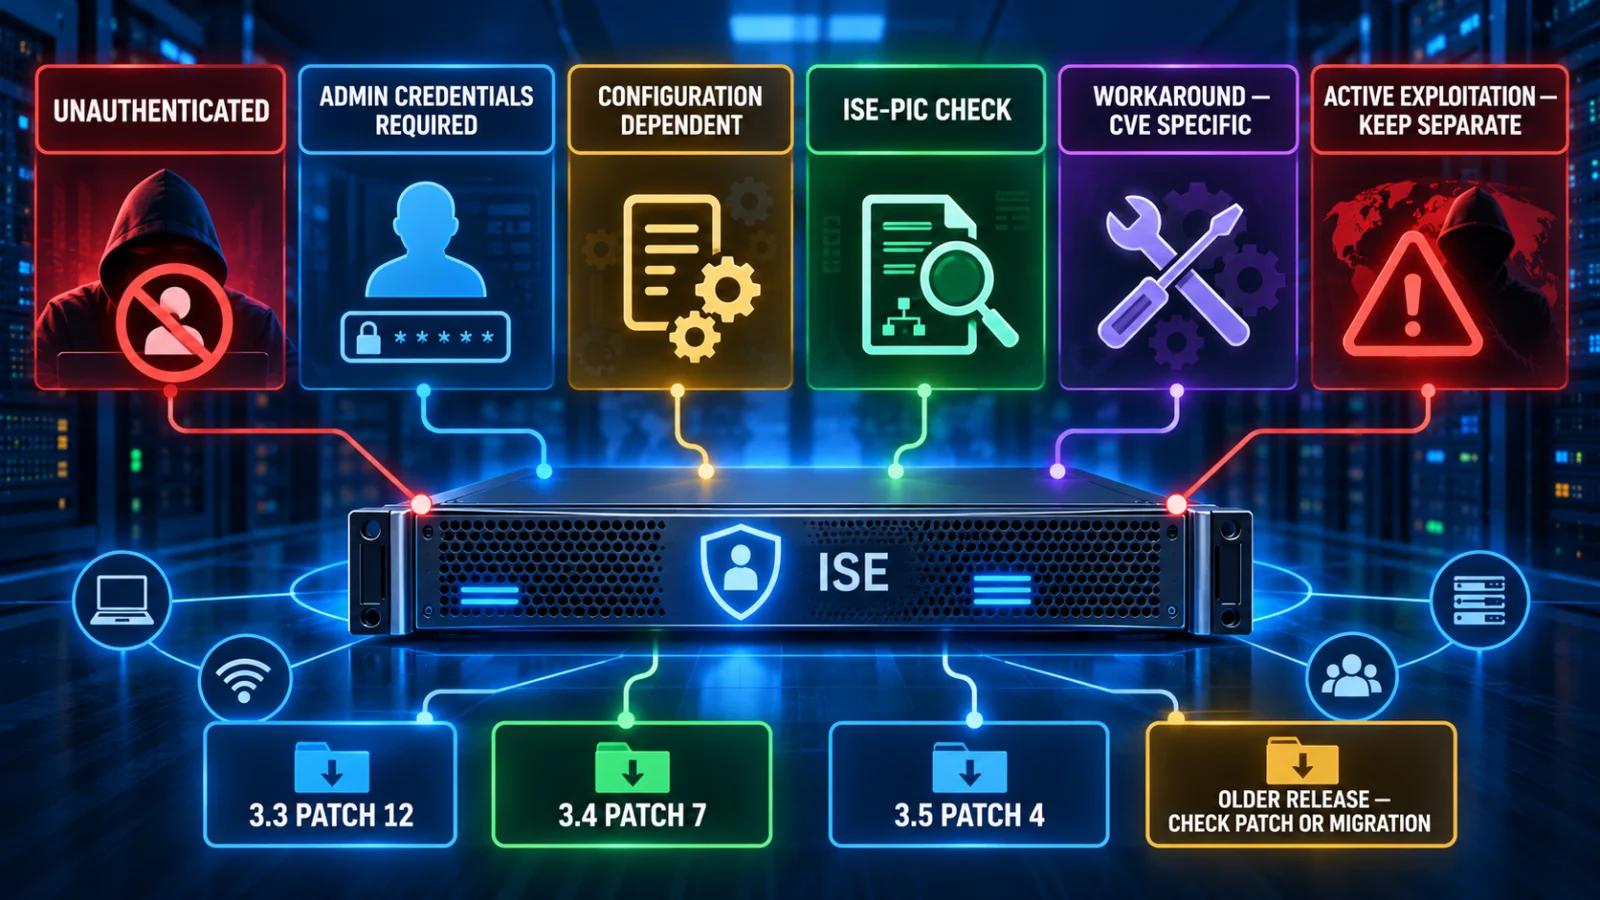
No. The September advisory set contains materially different attack prerequisites. CVE-2026-76423 is described in Cisco’s six-CVE advisory as an unauthenticated REST API authentication-bypass issue. By contrast, the separate remote-code-execution advisory covering CVE-2026-20176, CVE-2026-20211 and CVE-2026-20307 requires valid administrative credentials.
The command-injection advisory covering CVE-2026-20305 and CVE-2026-20306 also requires valid administrative credentials. Treating every Critical or High-severity entry as an unauthenticated internet-facing exploit would overstate the actual exposure.
Configuration matters for CVE-2026-20282, 20283 and 20284
Cisco’s authenticated RCE and API advisory has three different exposure states. CVE-2026-20282 does not depend on the same special configuration prerequisites as the other two. CVE-2026-20283 depends on the IPsec-related state described by Cisco, while CVE-2026-20284 requires SXP to be enabled with an SXP connection.
This is why TPS is not using a single generic ‘affected’ flag for the September batch. Administrators must check whether the relevant feature or configuration is present before deciding that a CVE applies.
Which September advisory has a workaround?
Cisco lists a workaround for CVE-2026-20283 in the authenticated RCE and API advisory. That workaround does not automatically apply to CVE-2026-20282 or CVE-2026-20284, and it should not be treated as a workaround for the wider September ISE advisory set.
For the other Critical advisories reviewed by TPS, Cisco’s primary remediation is fixed software rather than a batch-wide workaround.
What should ISE 3.3, 3.4 and 3.5 administrators target?
Across many of the Critical September advisories, the current Cisco tables converge on ISE 3.3 Patch 12, ISE 3.4 Patch 7 and ISE 3.5 Patch 4 as important fixed-release destinations.
That does not mean one row can replace Cisco’s individual advisory tables. Some CVEs have different first-fixed levels, and the 3.5 train in particular contains CVE-level differences in the authenticated RCE advisory. Use the common versions as a remediation baseline, then verify every applicable CVE against its own advisory.
What should ISE 3.1 and 3.2 administrators do?
Older trains require more care. Cisco provides 3.1 Patch 12 and 3.2 Patch 11 fixes for some vulnerabilities, while other CVEs in the same September family require migration to a later fixed release.
Cisco’s hardening guidance also recommends moving older maintenance-phase releases to a supported release that contains the full hardening set. Administrators on 3.1 or 3.2 should therefore avoid assuming that installing one final patch resolves every September advisory.
Does every advisory affect ISE-PIC?
No. Product applicability differs. Cisco’s advisory covering CVE-2026-20282, CVE-2026-20283 and CVE-2026-20284 states that ISE-PIC is not affected, while other September advisories do include ISE-PIC exposure.
Inventory whether the deployment is Cisco ISE, ISE-PIC or both before using a patch matrix.
Keep CVE-2026-76460 exploitation separate
CVE-2026-76460 is the September ISE authentication-bypass case associated with known active exploitation in Cisco’s current advisory context. That exploitation state must not be copied to unrelated vulnerabilities merely because they were published in the same September batch.
For the other reviewed advisories, Cisco generally states that its Product Security Incident Response Team was not aware of malicious use at the time of the reviewed advisory. One advisory also notes a public announcement without reporting known malicious exploitation.
Why one generic Cisco ISE patch row is unsafe
The September release contains six variables that materially change the remediation decision: exact CVE, product, release and patch level, authentication requirement, configuration prerequisite, workaround availability and exploitation state.
A deployment can therefore be exposed to one CVE but not another in the same advisory family. Likewise, one CVE may be fixed by installing a patch on the current train while another requires migration.
What Cisco ISE administrators should check now
- Record whether the deployment is ISE, ISE-PIC or both.
- Record the exact major release and installed patch level.
- Check every applicable September 16 advisory separately.
- Confirm whether the CVE requires authentication or administrative credentials.
- Check configuration prerequisites such as SXP or the relevant IPsec state where Cisco lists them.
- Do not apply a workaround from one CVE to another unless Cisco explicitly says it applies.
- Compare the deployment with the first fixed release for each applicable CVE.
- For older 3.1 and 3.2 deployments, determine whether Cisco requires migration rather than only another patch.
- Keep CVE-2026-76460’s active-exploitation response separate from non-exploited advisory states.
Bottom line
Cisco’s September 2026 ISE security release is a patch-matrix problem, not a single-vulnerability problem. Many Critical advisories point administrators toward 3.3 Patch 12, 3.4 Patch 7 and 3.5 Patch 4, but exact remediation still depends on the CVE, product, authentication state, enabled configuration and current release.
The safest approach is to inventory the deployment and work through each Cisco advisory individually. Do not infer active exploitation, unauthenticated access, ISE-PIC exposure or workaround availability across the whole batch.
Verification note
TPS reviewed Cisco’s September 16 ISE advance notice, ISE product security advisory list, hardening release and individual PSIRT advisories covering the Critical authentication-bypass, remote-code-execution, API and command-injection vulnerability groups.
Limitations and unresolved facts
Cisco may revise affected-release tables, fixed software, workaround guidance or exploitation status after publication. This article does not replace Cisco’s advisory-specific applicability checks for a production deployment. TPS also did not establish generic search-volume or Google Trends evidence for this query family.