






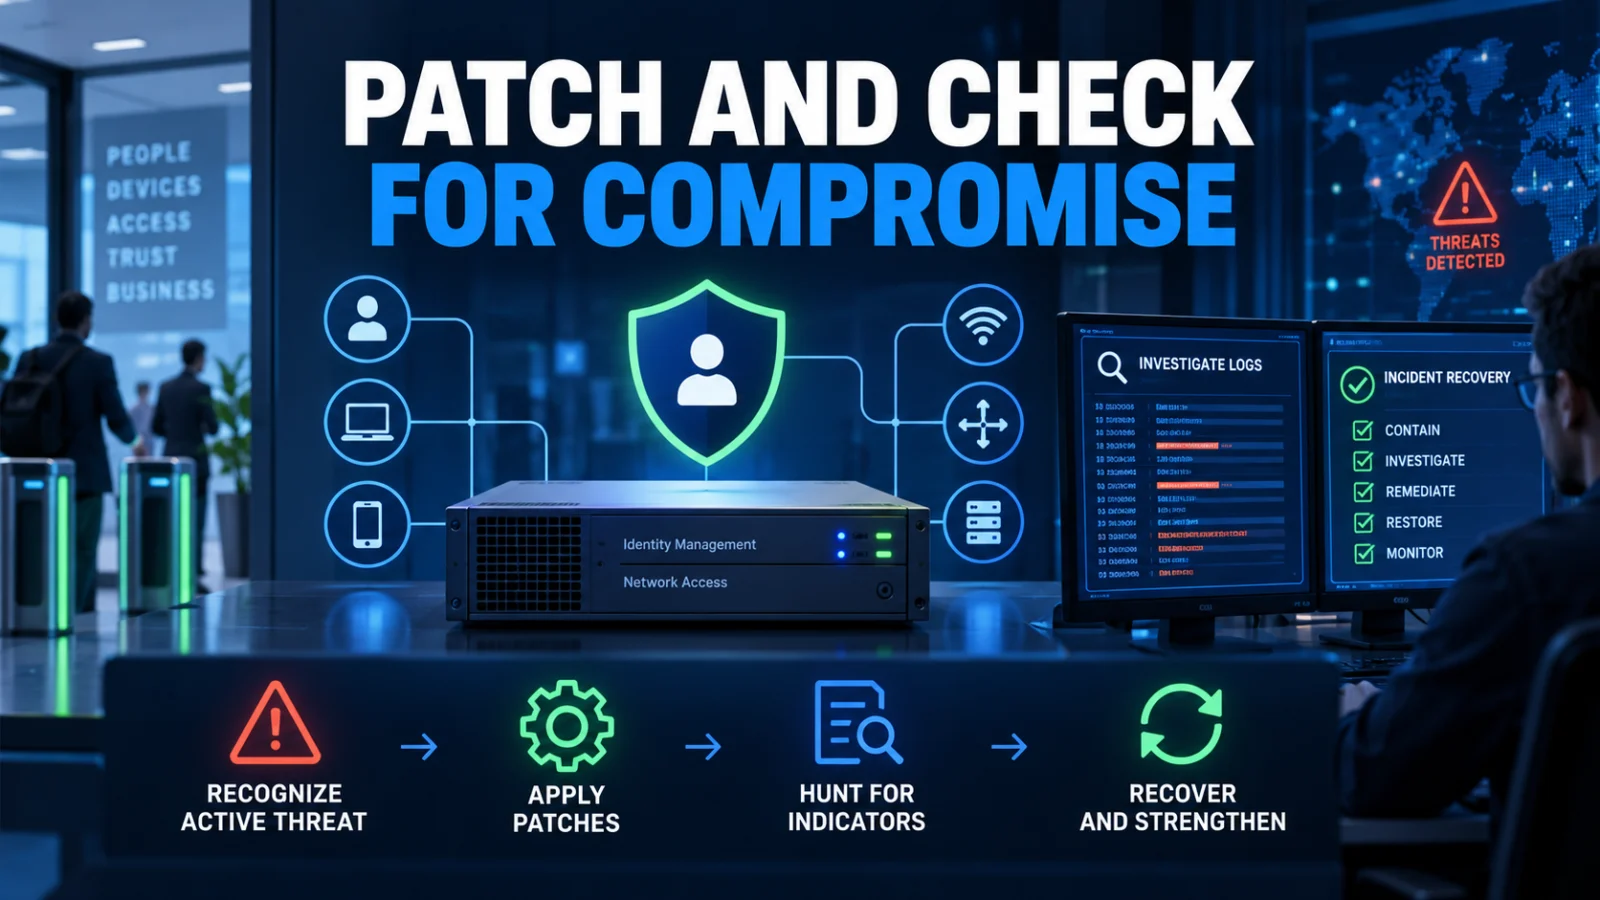
CVE-2026-76460 actively exploited is a critical Cisco Identity Services Engine security issue that requires two separate actions: upgrade affected ISE or ISE-PIC systems to a fixed release, then investigate whether exploitation may already have occurred. Cisco rates the authentication-bypass vulnerability CVSS 10.0, says it is aware of active exploitation and states that no workaround addresses the flaw.
The important boundary is that patching stops future exploitation of the fixed vulnerability but does not prove that a previously exposed node was never compromised. Cisco therefore provides both a remediation path and separate compromise-response guidance.
Confirm the exact Cisco ISE or ISE-PIC release and patch level on every relevant node before selecting the target patch.
Use Cisco’s current advisory to move to the first fixed patch or a later supported release for your branch.
Cisco says there is no workaround, but infrastructure ACLs can reduce remote exploitability by restricting management and control-plane traffic to authorized sources. Treat this only as temporary mitigation.
Review the documented ISE API gateway logs on every node and cross-check network or firewall telemetry outside the appliance.
Cisco strongly recommends re-imaging affected nodes and restoring from configuration backup when malicious activity is suspected.
Which Cisco ISE releases fix CVE-2026-76460?
Cisco lists the following first fixed releases for the supported ISE and ISE-PIC branches:
| Release | First fixed release |
|---|---|
| 3.1 | 3.1 Patch 12 |
| 3.2 | 3.2 Patch 11 |
| 3.3 | 3.3 Patch 12 |
| 3.4 | 3.4 Patch 7 |
| 3.5 | 3.5 Patch 4 |
Cisco says ISE 3.0 has reached End of Software Maintenance. Customers still on that branch should migrate to a supported release containing the fix rather than treating 3.0 as a branch awaiting another security patch.
What does CVE-2026-76460 allow?
Cisco says an unauthenticated remote attacker can exploit the vulnerability through a crafted request to an affected API endpoint and bypass authentication. Successful exploitation may allow command execution with root-level privileges.
Cisco states that ISE and ISE-PIC are affected regardless of device configuration. That does not mean every deployment is equally reachable from an attacker; network exposure and access controls still determine whether the vulnerable interface can be reached.
Is there a workaround for CVE-2026-76460?
No. Cisco states that there are no workarounds that address the vulnerability.
Cisco does document a mitigation using infrastructure access control lists. Administrators can restrict management and control-plane traffic destined for the affected device so that only authorized source networks can reach it. This can reduce remote exploitability while patching is completed, but it does not remove the vulnerability and should not replace the fixed software release.
How to check Cisco ISE for possible exploitation
Cisco instructs administrators to inspect the ISE API gateway access log, ise-kong/access.log, for suspicious usernames. The check should be performed on every node in a distributed deployment because reviewing only one node can leave activity on another node unseen.
Cisco provides a non-exhaustive example using:
show logging application ise-kong/access.log | include dummyuser
The example username is an indicator to search for, not a complete list of malicious activity. Absence of that exact string must not be treated as proof that exploitation did not occur.
Why external firewall and network logs matter
Cisco warns that an attacker who obtains root-level access may be able to remove or hide evidence on the affected ISE node. Administrators should therefore cross-check logs outside the appliance, including firewall and network telemetry, for unusual connections, unexpected external uploads or downloads and other activity inconsistent with normal ISE behavior.
If longer local history is needed, Cisco’s advisory describes obtaining additional access logs through the support-bundle process.
What if you find suspicious activity?
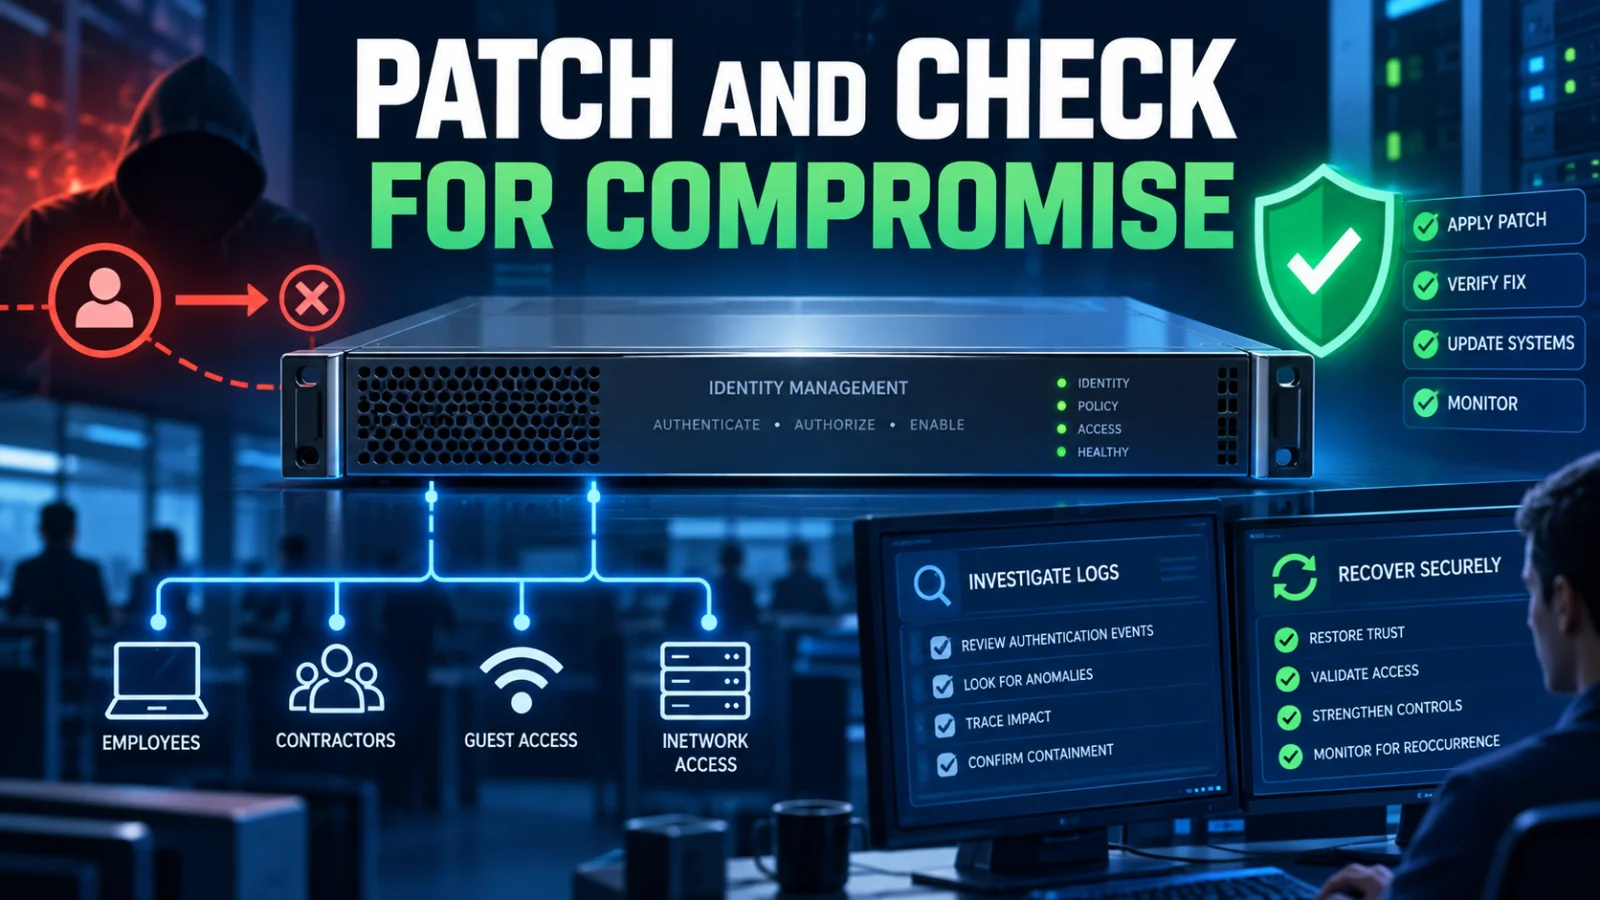
If the documented log review or other evidence suggests malicious activity, Cisco strongly recommends re-imaging the affected nodes and restoring their configuration from backup.
This is different from simply installing the security patch. The patch closes the vulnerability going forward; re-imaging and restoration address the possibility that an attacker already gained privileged access and left changes or persistence behind.
Does installing the patch prove Cisco ISE is clean?
No. A fixed release proves that the known vulnerability has been remediated for future exploitation under Cisco’s current guidance. It does not establish that a previously exposed deployment was never compromised.
The same caution applies to the documented IOC example. Cisco explicitly notes that attackers with root access may remove or conceal evidence, so incident responders should use multiple evidence sources rather than interpreting one clean local log search as definitive clearance.
Who is exploiting CVE-2026-76460?
Cisco confirms active exploitation but has not publicly established the attacker identity, victim count, complete exploitation timeline or full geographic distribution in the reviewed advisory. TPS therefore does not attribute the activity to a named group or infer the scale of compromise from the existence of the vulnerability alone.
What administrators should monitor next
Recheck Cisco’s advisory if the fixed-release table changes, Cisco publishes additional indicators of compromise, the recovery guidance changes or new exploitation evidence materially changes the incident-response requirements.
Verification method
ThePulseSignal reviewed Cisco’s CVE-2026-76460 security advisory and Cisco’s September 2026 ISE hardening guidance, then cross-checked current security reporting to separate the exact fixed-release path, temporary iACL mitigation and compromise-response workflow.
Limitations and unresolved facts
Public evidence does not establish a complete victim count, attacker identity, exploitation start date, campaign geography or exhaustive set of indicators. Cisco may revise the affected-release, IOC or recovery guidance as investigation continues.