






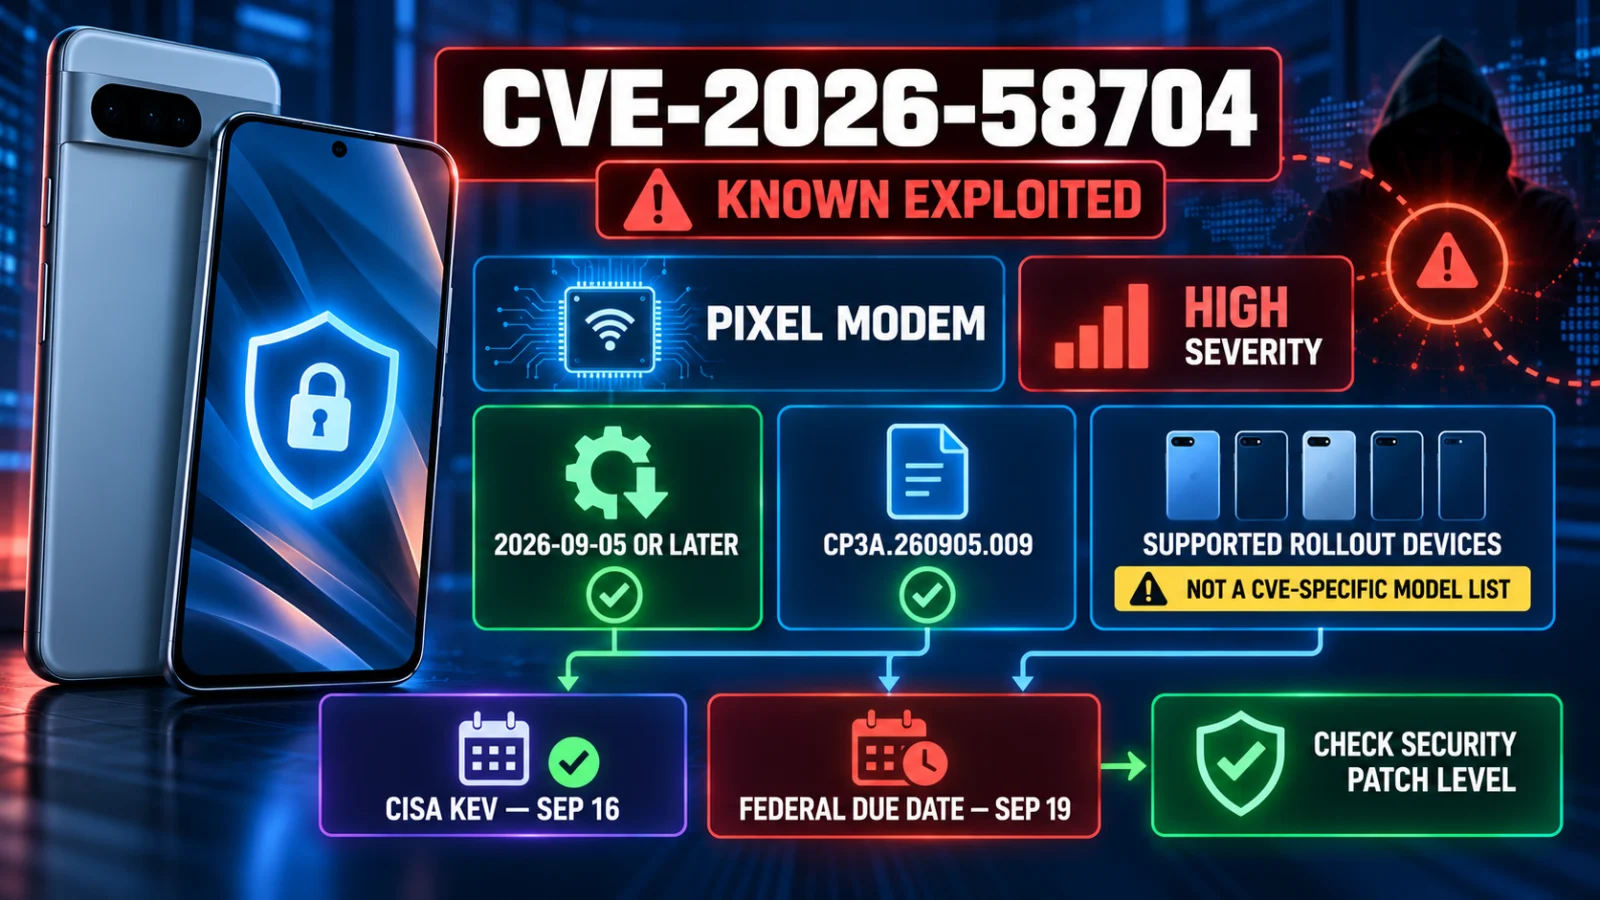
CVE-2026-58704 Pixel security guidance now has a clear verification point: Google says security patch level 2026-09-05 or later addresses all issues in its September 2026 Pixel Update Bulletin, including CVE-2026-58704. CISA added the vulnerability to its Known Exploited Vulnerabilities catalog on September 16 and lists September 19 as the remediation due date under the applicable federal directive workflow.
Google classifies CVE-2026-58704 as a High-severity elevation-of-privilege vulnerability in the Pixel modem component and says there are indications that it may be under limited, targeted exploitation. The main reader task is therefore to verify the phone’s actual security patch level rather than infer safety from the device name alone.
Direct answer: If a supported Pixel shows security patch level 2026-09-05 or later, Google’s September Pixel bulletin says the vulnerabilities in that bulletin are addressed. Google’s separate September rollout notice lists global build CP3A.260905.009 for its supported-device rollout, but that device roster is not a CVE-2026-58704-specific affected-model list.
What is CVE-2026-58704?
CVE-2026-58704 is a Google Pixel modem vulnerability involving an authorization or permission-check logic problem that can lead to elevation of privilege. Google’s bulletin rates it High severity and places it in the Modem subcomponent.
The published vulnerability metadata says exploitation does not require user interaction. The available attack-vector metadata describes a proximal or adjacent-network condition rather than a conventional unrestricted internet-remote attack, so TPS does not describe this as an ordinary remote internet exploit.
What Pixel security patch level fixes CVE-2026-58704?
Google states that security patch level 2026-09-05 or later addresses all vulnerabilities in the September 2026 Pixel Update Bulletin. Because CVE-2026-58704 appears in that bulletin, this is the controlling remediation state for the article.
| Verification item | Current evidence-backed value |
|---|---|
| Vulnerability | CVE-2026-58704 |
| Component | Pixel Modem |
| Severity | High |
| Impact class | Elevation of privilege |
| Fixed security patch level | 2026-09-05 or later |
| CISA KEV date added | 16/09/2026 |
| CISA remediation due date | 19/09/2026 |
What September Pixel build did Google publish?
Google’s separate September software-update announcement lists global build CP3A.260905.009 for the supported Pixel rollout. Google says rollout timing can vary by carrier and device.
The supported-device roster in that rollout includes Pixel 6, Pixel 6 Pro, Pixel 6a, Pixel 7, Pixel 7 Pro, Pixel 7a, Pixel Fold, Pixel Tablet, Pixel 8, Pixel 8 Pro, Pixel 8a, Pixel 9, Pixel 9 Pro, Pixel 9 Pro XL, Pixel 9 Pro Fold, Pixel 9a, Pixel 10, Pixel 10 Pro, Pixel 10 Pro XL, Pixel 10 Pro Fold and Pixel 10a.
Are all of those Pixel models confirmed affected by CVE-2026-58704?
No model-by-model CVE applicability table was published in the recovered Google Pixel bulletin. Google’s software-update roster establishes which supported devices receive the September rollout; it does not establish that every listed model contains the vulnerable modem implementation.
This distinction matters particularly for devices such as the Pixel Tablet. TPS does not infer that a device is vulnerable merely because Google included it in the September software rollout.
How to check whether your Pixel has the fix
Open your Pixel’s security or Android update information and confirm that the Android security patch level is 2026-09-05 or later.
If your supported Pixel is still on an earlier patch level, install Google’s current available system update and recheck after the device restarts.
Google has not published a CVE-specific affected-model matrix, so model ownership alone is not enough to determine vulnerability or remediation state.
The security patch level is the controlling CVE remediation evidence. CP3A.260905.009 is Google’s listed global September rollout build, subject to carrier and device rollout differences.
Enterprise and government administrators should confirm that targeted devices actually received the fixed patch rather than assuming update availability means deployment succeeded.
CISA marks forensic triage as required under its federal workflow. Other organizations should follow their own current security and regulatory obligations.
What does the CISA September 19 deadline mean?
CISA’s KEV entry lists September 19, 2026 as the remediation due date under the applicable federal directive framework. That date should not be presented as a universal legal deadline for every private Pixel owner.
For general users and private organizations, KEV inclusion is still strong prioritization evidence because CISA reserves the catalog for vulnerabilities with evidence of exploitation. The specific compliance obligation, however, depends on the organization and governing policy.
Does CISA require forensic triage?
Yes. The KEV record marks forensic triage as required under the applicable federal workflow. That increases the importance of treating the vulnerability as more than a routine monthly patch issue in managed government environments.
The recovered Google bulletin does not provide a complete device-level compromise test or exhaustive forensic procedure for general Pixel owners. TPS therefore does not claim that a normal-looking phone, antivirus scan or factory reset proves whether exploitation occurred.
Is CVE-2026-58704 part of the general Android September bulletin?
The vulnerability is documented in Google’s Pixel Update Bulletin, which covers Google-device-specific issues in addition to the broader Android Security Bulletin. That makes the Pixel bulletin the controlling source for this CVE’s patch state.
TPS already treats the broader Android September update as a different reader job: checking whether an Android device has received the full monthly security level. This page instead answers the Pixel-specific known-exploited vulnerability and KEV verification task.
What remains unknown
Google has not published a CVE-2026-58704-specific affected-model or modem-hardware matrix. Public evidence also does not establish the victim count, attacker identity, exploitation start date, campaign geography or exhaustive forensic indicators.
Those unknowns do not prevent a safe current action because Google’s remediation state is explicit: supported Pixel devices should be updated until the device reports security patch level 2026-09-05 or later.
What happens next?
The next material checkpoint is September 19, the remediation due date in CISA’s KEV workflow. TPS should also update this page if Google publishes a model-applicability clarification, changes the fixed patch level or rollout build guidance, or if Google or CISA releases materially new exploitation or forensic-response information.
Verification method
ThePulseSignal reviewed Google’s September 2026 Pixel Update Bulletin, Google’s September Pixel software-rollout notice and the CISA KEV state, then reconciled the difference between the fixed security patch level, the supported-device rollout list and the federal remediation deadline.